Tech
What Are Spoof SMS Messages? The Complete Guide to How They Work and Why They’re Dangerous

Every day, businesses and individuals receive text messages from numbers or names they recognize — banks, delivery companies, government agencies, employers. Most people read these messages without question. That implicit trust is precisely what makes SMS spoofing one of the more consequential threats in modern communications. The problem is not new, but the scale and sophistication at which it now operates have changed considerably. Organizations that rely on SMS for customer communication, internal alerts, or authentication workflows face a real and growing risk of being impersonated — or of having their staff and customers deceived through messages that appear entirely legitimate.
Understanding how this works, why it succeeds, and what conditions make it difficult to detect is not a technical exercise reserved for security professionals. It is practical knowledge for anyone responsible for communications infrastructure, customer trust, or organizational risk.
What Spoof SMS Messages Are and How They Function
The term spoof sms messages refers to text messages that are sent with a falsified sender identity. Instead of displaying the actual originating number or platform, the recipient sees a name, number, or shortcode that belongs to someone or something else entirely. This is not a vulnerability in the traditional sense — it is a feature of how SMS infrastructure was originally designed, now exploited for deceptive purposes.
For a more structured understanding of how this threat is categorized and tracked across industries, resources covering spoof sms messages provide useful context on the types and mechanisms involved. The core technical reality is that the global SMS routing system was built during an era when sender verification was not a priority. Messages travel through a chain of interconnected carriers and aggregators, and in many cases, the sender field is simply accepted at face value.
The Mechanics Behind Sender ID Manipulation
When a message is transmitted through an SMS gateway, the sending platform typically has the ability to define what appears in the “From” field. Legitimate businesses use this capability to display their brand name instead of a raw phone number. The same infrastructure, however, can be used by bad actors to display any name or number they choose — including the name of a bank, a delivery carrier, or an employer.
In many countries, there is limited or no technical enforcement at the carrier level to verify whether the entity claiming a particular sender name or number actually owns it. The verification gap exists not because of negligence but because the SMS protocol was standardized before the current threat environment existed. The result is that two-way verification — confirming both sender and recipient identity — is not a default feature of standard SMS delivery.
How Spoofed Messages Enter Legitimate Conversation Threads
One of the more disorienting aspects of SMS spoofing is that spoofed messages can appear inside the same conversation thread as genuine messages from the entity being impersonated. On most mobile devices, messages are grouped by sender name or number. If an attacker sends a message using the same alphanumeric sender ID as a bank, the phone will display that message alongside real previous messages from that bank. The recipient has no visible way to distinguish between them at a glance.
This thread-injection effect is particularly effective in scenarios involving two-factor authentication, package delivery updates, or account alerts — situations where people are already expecting a message and where a prompt to click a link or confirm information feels routine rather than suspicious.
Why SMS Spoofing Succeeds as a Deception Method
The effectiveness of spoofed SMS messages does not rest on technical complexity alone. It depends heavily on behavioral patterns and the assumptions people bring to their reading of text messages. SMS as a channel carries a level of implicit credibility that email no longer does. Most people have been trained, over years, to treat suspicious emails with caution. Text messages have not been subjected to the same collective skepticism, even though they carry equivalent risk.
The Role of Context and Timing
Spoofed messages are most effective when they arrive at moments of heightened relevance. A message appearing to come from a delivery company arrives the day after an online purchase. A message from a bank arrives during a period when fraud alerts are common. A message from an employer’s HR system arrives at the start of a payroll cycle. These contextual matches are not always coincidental — attackers frequently harvest data from breaches, public records, or social media to time and personalize their messages.
When a message aligns with something the recipient is already thinking about, the normal friction of critical evaluation is reduced. The message feels expected, which makes it feel trustworthy.
The Absence of Visible Red Flags
Phishing emails often contain grammatical errors, mismatched domains, or formatting inconsistencies that trained eyes can identify. Spoofed SMS messages do not carry the same volume of visible signals. A short message with a plausible instruction and a link can be composed correctly and compactly with very little effort. The brevity of SMS as a format actually works in the attacker’s favor — there is simply less content to scrutinize.
Recipients are also rarely in a position to verify the sender independently in the moment. Unlike email, where hovering over a sender address reveals the underlying domain, SMS offers no equivalent transparency layer on most standard devices and messaging applications.
The Industries and Contexts Most Exposed
While no sector is immune, certain industries face disproportionate exposure because of how heavily they rely on SMS for time-sensitive communications. According to research documented by the Federal Trade Commission, impersonation through digital messaging channels has become one of the most consistently reported fraud mechanisms, with financial losses concentrated in sectors where trust and urgency are both high.
Financial Services and Banking
Banks and financial institutions are among the most impersonated entities in SMS spoofing campaigns. The combination of high trust, financial stakes, and familiar messaging patterns — transaction alerts, one-time passcodes, fraud warnings — makes this sector a reliable target. Customers who receive a message appearing to come from their bank and prompting them to verify a transaction or confirm account details are operating within a mental model that has been deliberately replicated by the attacker.
The damage in these cases extends beyond individual financial loss. Institutions face reputational harm when customers associate the brand with deception, even when the institution itself was the impersonated party rather than the origin of the deceptive message.
Logistics, Retail, and Public Services
Delivery notifications and order confirmations represent another high-volume target area. The expectation of receiving package updates is so normalized that recipients rarely pause to assess whether a specific message is genuine. Attackers use this pattern to insert phishing links into what looks like routine shipment communication.
Public services — including healthcare providers, local government communications, and utility companies — are also frequently impersonated, particularly during periods of elevated public attention such as tax season, public health events, or infrastructure disruptions. The authority associated with these entities increases compliance with whatever action the message requests.
Organizational Risk Beyond the Individual Victim
It is a common assumption that SMS spoofing primarily harms individuals. In practice, the organizational risk is substantial and often underweighted. When an attacker successfully impersonates a company, several things happen simultaneously: customers are harmed, brand trust erodes, and in some regulatory environments, the impersonated organization may face scrutiny around its communication security posture.
Internal Spoofing and Workforce Exposure
Spoofed messages are not exclusively directed at customers. Internal attacks, where employees receive messages appearing to come from HR systems, payroll platforms, IT departments, or executive leadership, represent a distinct and consequential threat. An employee who receives a message appearing to come from their company’s IT team asking them to reset credentials or confirm access details is navigating the same deceptive mechanics as a banking customer — with equally serious potential consequences for the organization.
Business email compromise has been widely discussed in corporate security contexts, but its SMS equivalent receives less structured attention despite operating through the same psychological mechanisms.
Compliance and Liability Considerations
Organizations that use SMS for regulated communications — healthcare appointment reminders, financial disclosures, identity verification — carry some responsibility for ensuring their communication channels are not easily weaponized against the people they serve. In environments governed by data protection frameworks, the use of SMS without adequate sender authentication measures can attract regulatory attention if a breach occurs through that channel. The regulatory expectation is not that organizations prevent all external spoofing, but that they have taken reasonable measures to secure their communications and educate their audiences.
Detection, Awareness, and Structural Responses
Addressing SMS spoofing effectively requires understanding that no single countermeasure eliminates the risk entirely. The structure of global SMS routing means that technical mitigations exist at different layers — carrier-side filtering, application-level verification, and end-user awareness all contribute to reducing exposure without individually resolving it.
What Carrier-Level Measures Can and Cannot Do
Some telecommunications providers have introduced filtering systems that attempt to flag or block messages from sources that display characteristics consistent with spoofing. These systems vary significantly in effectiveness and coverage. International messages in particular pass through multiple carriers before reaching a recipient, which creates points in the chain where filtering may not be applied consistently. Organizations that send legitimate high-volume SMS communications benefit from registering their sender IDs with carriers in jurisdictions where such registration is available, as this reduces the ease with which their identity can be replicated.
Building Awareness at the Organizational Level
For organizations that communicate with customers or staff via SMS, building structured awareness around what their messages will and will not contain is a practical measure. Clearly communicating to customers that the organization will never request passwords, payment information, or one-time codes via SMS response — and reinforcing this across all genuine communications — establishes a behavioral baseline that makes spoofed requests easier to identify.
Staff training that addresses SMS-based impersonation alongside email phishing and voice-based social engineering creates a more complete security awareness framework. The same critical thinking that employees are trained to apply to suspicious emails should extend consistently to unexpected or unusual text messages, regardless of how familiar the sender name appears.
Closing Perspective
SMS spoofing is neither a niche technical problem nor a threat that only affects careless individuals. It operates at the intersection of trusted infrastructure, human behavior, and inadequate sender verification — conditions that are not easily resolved by any single change in technology or policy. The persistence of the threat reflects how deeply embedded SMS has become in both personal and organizational communication workflows, and how little the underlying protocol was designed for an environment where trust could not be assumed.
For businesses, the practical response involves both structural awareness and honest assessment of how SMS is used within their communications ecosystem. Understanding how spoofing works — not in abstract terms, but in the specific contexts where it tends to succeed — is the foundation of any meaningful response. Organizations that take the time to understand this threat, communicate clearly with the people they serve, and advocate for stronger sender verification across their carrier relationships are better positioned to limit the damage when spoofed campaigns inevitably use their identity. The goal is not elimination of a risk that is architecturally embedded in the channel, but deliberate, consistent reduction of its impact on the people who depend on receiving legitimate communications.


Welding puts more stress on protective gear than almost any other trade. Molten spatter, radiant heat, sparks that arc in unpredictable directions, and hours of friction against a bench all add up fast. Yet a lot of welders are wearing an apron that looks the part but quietly fails the moment it matters.
The problem is that apron damage is rarely obvious until it’s too late. A weak spot doesn’t announce itself — it just lets a spark through at the worst possible moment. Below are five warning signs that your current apron may not be doing its job, and what to look for in a replacement.
It Scorches, Chars, or Melts Instead of Resisting Heat
Run your hand over the apron after a session. If you find small burn marks, hardened or glazed patches, or areas where the surface has gone stiff and brittle, the material is absorbing damage it shouldn’t be.
This is usually a sign the apron isn’t made from real leather at all — or that it’s a lower grade that can’t take sustained heat exposure. A proper leather apron for welding should shrug off short contact with sparks and spatter without scorching through. If yours is showing char marks after every use, the material is degrading faster than it should, and each burn mark is a thinner spot the next spark can pass straight through.
You Can See or Feel Layers Peeling Apart
Pick up the edge of the apron and flex it slightly. If you notice separation — a top layer starting to lift, flake, or peel away from a backing material underneath — you’re dealing with bonded or reconstituted leather, not a single piece of hide.
Bonded leather is made from scraps of leather fiber glued together with a polyurethane coating. It looks convincing on a store shelf, but heat and constant flexing break down that adhesive layer quickly. Once it starts peeling, it only gets worse, and the protective barrier becomes inconsistent across the apron. A genuine full grain leather apron, by contrast, is cut from a single hide with the natural grain intact — there’s no glue layer to fail, so it doesn’t delaminate under heat and repeated bending.
The Stitching Is Single-Row, Uneven, or Already Fraying
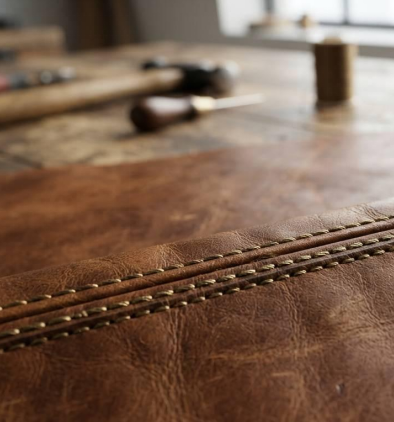
Stitching takes as much abuse as the leather itself, especially at stress points like the neck strap, waist ties, and pocket seams. If your apron uses a single row of stitching, has visibly uneven spacing, or already shows loose or broken threads after a few months, it’s a weak point waiting to fail.
Look for double-stitched seams at every load-bearing point. This isn’t just about longevity — a seam that rips open mid-shift can let the apron shift out of position exactly when you need full coverage. Reinforced stitching is one of the easiest things to check before buying, and one of the most commonly cut corners on cheaper aprons.
Hardware Is Rusting, Bending, or Already Broken
Cheap rivets, buckles, and D-rings are usually plated rather than solid metal. Under welding heat and shop humidity, that plating wears off fast, and what’s underneath starts to rust, bend, or snap. A broken buckle or a rivet that’s pulled loose from the leather isn’t just an inconvenience — it can mean straps that won’t stay adjusted, pockets that won’t hold tools securely, or an apron that shifts and exposes skin mid-task.
Solid brass hardware costs more to manufacture, which is exactly why manufacturers cut it first on budget aprons. If your hardware is showing rust spots or has already failed once, treat it as an early warning that the rest of the build quality is probably just as compromised.
It’s Thin Enough to See Light Through, or Flexes Like Fabric
Hold the apron up to a light source. If you can see light coming through the leather, or if the material folds and drapes more like heavy fabric than like leather, it’s too thin to offer real spark and heat protection.
Weld-grade protection generally calls for leather in the 1.2mm–1.6mm range — thick enough to absorb heat and resist punch-through from spatter, but still flexible enough to move with you over a full shift. Thinner leather (often marketed as “genuine leather” rather than full grain) is split or sanded down during processing, which strips away the dense, protective outer layer of the hide. A full grain leather apron keeps that outer layer intact, which is what gives it both the thickness and the natural resistance that thinner, processed leather can’t match.
What to Look for Instead
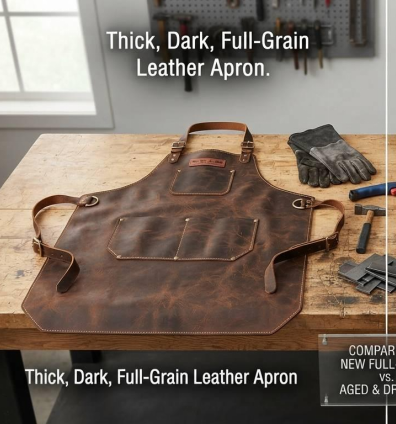
If your current apron is showing two or more of these signs, it’s not a maintenance problem — it’s a replacement problem. When shopping for a new one, prioritize:
- Full-grain cowhide, not bonded or heavily processed “genuine leather”
- 1.2mm–1.6mm thickness for real heat and spark resistance
- Double-stitched seams at every stress point
- Solid brass hardware, not plated metal
- Adjustable straps that let the apron sit close to the body without gaps
A well-made leather apron for welding isn’t just a uniform piece — it’s the last layer between you and a spark that’s traveling toward your skin. Worn-out gear is easy to overlook because the damage builds gradually, but the signs above are your apron telling you it’s already behind on the job.

Modern enterprises use numerous systems, servers, and devices, and they must all function properly. In complex IT environments, manually setting up and modifying these systems is laborious, repetitive, and prone to human error. Configuration automation comes into play here, enabling businesses to quickly and accurately manage their IT operations. Automation allows you to perform repetitive tasks reliably without human intervention for each little adjustment. Businesses can reduce mistakes, save time, and achieve more consistency and stability across their technology environment by automating routine configuration tasks.
1. Reducing Human Error in Daily Operations
A huge advantage of configuration automation is the minimization of human error. If engineers are manually configuring every day, tiny mistakes can eventually develop that could cause major issues. Automation removes this chance by always following set directions with no fatigue and distractions. Regardless of who started the process, this consistency guarantees that systems operate precisely as intended. Reduced errors result in fewer interruptions, and less troubleshooting, as well as more assurance in day-to-day operations.
2. Saving Valuable Time Across Teams
Hours that could be used for more productive work are frequently wasted on manual configuration procedures. Automation swiftly completes tedious setup procedures, allowing technical teams to concentrate on creativity in addition to problem-solving. Automated scripts can finish the same operation in minutes rather than requiring a whole day to configure similar systems one by one. Large-scale rollouts and urgent system changes make this time efficiency extremely essential. Operational tasks no longer consume teams, allowing them to focus on strategic goals.
3. Maintaining Consistency Across Systems
Inconsistencies are nearly inevitable when several systems are manually configured.
Automation allows you to standardize every server, device, and application to the same baseline configuration. Standardization is key for multi-site organizations and larger networks. It’s much easier to find problems, push updates, and ensure compliance with internal policies when everything is configured the same. Manually recording these variations becomes a laborious and error-prone operation in the absence of technology. A standardized environment strengthens the foundation for smoothly scaling operations as the business expands, streamlines management, and increases dependability.
4. Closing Security Gaps with Automation
Out-of-date or incorrectly configured systems leave gaps in your security. Automation lets you quickly and consistently apply security settings to close that gap. Automated procedures can implement security regulations instantly rather than waiting for manual updates, lowering exposure to possible attacks. In large environments with plenty of endpoints, this proactive strategy reduces the likelihood of oversight. It’s also easy to identify when someone has made unauthorized changes with automation. If something is different than how it’s configured to be, you’ll know. Automation can significantly improve your organization’s security.
Conclusion
For businesses looking to improve productivity, consistency, and security in complex IT settings, configuration automation has become crucial. Businesses can further automate their operations with Opkey by utilizing a single Cloud Application Lifecycle Management (CALM) platform driven by Argus AI. Opkey automates configuration, testing, impact analysis and training for Oracle, Workday, Salesforce, Coupa and more business applications so teams can confidently embrace change. The no-code AI automation platform helps businesses operate simpler, become more dependable and continuously improve enterprise applications across their lifecycle by decreasing manual effort up to 80%, cutting go-live schedules by 30% and mitigating risk of downtime by 92%.
You have great products, but they aren’t fetching you customers. They may be browsing and adding stuff to their cart. But they leave right before paying.
A lot is actually going wrong on your checkout page to cause this.
A shipping fee might show up too late. A form might ask for too many details before someone can pay. Sometimes your checkout might show payment methods your customers don’t prefer. Moreover, the experience might not be smooth on their mobiles.
Switching to a new ecommerce checkout solutions provider won’t change things overnight. You need to understand the problems impacting your revenue in depth. Let’s begin.
1. Too Many Steps at Checkout
Picture this. A customer loves your products and is ready to buy some. Just when they were about to complete the payment, your checkout page throws in lots of tricky steps. This can be requesting a password with strict rules or adding a CAPTCHA or “verify you are human” check.
That’s just going to make the checkout process annoying.
Start by cutting your checkout down to what’s essential. Keep it to a name, address, payment details, and confirmation. Nothing else belongs on that screen. Make sure shipping costs, taxes, and any fees are displayed on the product page or cart before checkout begins.
The page must have autofill for country/location based on the shipping address. Don’t just place a long dropdown country selector. You can add a shipping calculator that updates in real time. If you offer free shipping past a certain order value, let customers know that early on.
2. Payment Options Customers Don’t Fancy
A customer can love your product, breeze through your checkout, and still walk away because you didn’t offer a payment method they’d like. You see, buy-now-pay-later options and digital wallets aren’t extras anymore. They are the norm now.
But there are other related problems you need to tackle.
A card might get declined for no real reason, or billing details may not match what the issuer expects. A subscription renewal can also fail. Customers don’t think twice before leaving when these things happen. Here’s what to do.
- Include UPI, major cards, digital wallets like Apple Pay and Google Pay, and a BNPL option.
- Clean up your payment processor data. It must have consistent billing formats, correct customer details, and recognizable merchant descriptors.
For subscriptions, use smart retry logic and card updater functionality to make payments more seamless.
3. The Mobile Conversion Gap
The global mobile e-commerce market might be worth $5,009.99 billion by 2034. So, a large part of your traffic now already comes or will come from phones in the future. But if you’re still losing buyers, there are issues in your store’s mobile UX.
Look carefully at your store design. Ensure the buttons, dropdowns, and form fields have enough space to tap accurately on the first try. Autofill should handle names, addresses, and card details, cutting typing down to almost nothing.
For digital wallets like Apple Pay and Google Pay, you must offer buyers a super smooth interface to pay. They must not be typing a sixteen-digit card number on a phone keyboard.
Test the entire flow on an actual phone, not just a resized browser window. Use Android and Apple devices for testing. Many issues don’t stand out on a desktop, like a keyboard covering a button or buttons that appear too small on a phone screen.
4. Forcing an Account Creation
A customer who’s ready to pay can leave if the only path forward is creating an account first.
What’s the best way to solve this? Make guest checkout the default option. Put it at the front and center, and ask for account creation only after they place the order. This will let you track shipping or speed up the process next time.
You can offer quick one-click logins via their social media accounts, Google, or Apple accounts. Save their shipping and payment details securely during checkout. It’ll help buyers switch to a complete account later.
If you need customer data for marketing, collect their email addresses during guest checkout. Most customers create a full account if they like shopping from your store. But it’s all up to how your checkout treats them!
Run This Quick Checkout Audit
Before making any big changes, walk through your own checkout like a first-time buyer and look out for these:
- See your checkout loading time. It must not be more than 3 seconds.
- Try entering an incorrect or expired card number to check if you get an error message telling you what’s wrong.
- Add items to the cart. Check your cart after some time to see if it still contains those items.
- Look for glitchy coupon codes, since they can send people off to search for a discount instead of finishing the payment.
- You also need to confirm that the order confirmation page and email have complete order details. This must have product info, charges, and the expected date of arrival.
Most importantly, put yourself in the shoes of your buyer to see how the shopping experience actually feels. Gather inputs from your team about this. To get the best out of your checkout, you can consult CodeClouds. They’ve been offering custom checkout solutions for years across a variety of projects, so they have the expertise to solve your problems.

The Enduring Appeal of Batman: Why Every Generation Finds Its Own Dark Knight

Top Digital Marketing Agencies for Multi-Channel Campaign Success

How Technology Is Changing the Way We Learn to Drive

Keeping Dogs Clean After Muddy Outdoor Adventures

Improving Business Operations Through Service and Asset Management

Bond Street Area Rentals: A Neighbourhood Guide for First Time Luxury London Visitors

The 15 Highest-Paid Rugby Players in the World
Christopher Dare: The Untold Story of Engineer and Former Husband of Angela Rippon

How to Ensure Your Home is Valued Correctly for a Quick Sale

What Is Fanquer? The Digital Creator Platform Transforming Direct-to-Fan Engagement

Dr Jared Ross: Missouri Appeals Court Upholds Protection Order Over Graphic Torture and Murder Threats
Nancy Hallam: The Inspiring Life, Career, and Success Story Behind Ian Wright’s Wife
The 15 Highest-Paid Rugby Players in the World
Christopher Dare: The Untold Story of Engineer and Former Husband of Angela Rippon
How to Ensure Your Home is Valued Correctly for a Quick Sale
What Is Fanquer? The Digital Creator Platform Transforming Direct-to-Fan Engagement
Dr Jared Ross: Missouri Appeals Court Upholds Protection Order Over Graphic Torture and Murder Threats
Nancy Hallam: The Inspiring Life, Career, and Success Story Behind Ian Wright’s Wife
-
 Sports4 months ago
The 15 Highest-Paid Rugby Players in the World
-
Celebrity10 months ago
Christopher Dare: The Untold Story of Engineer and Former Husband of Angela Rippon
-
 Real Estate8 months ago
How to Ensure Your Home is Valued Correctly for a Quick Sale
-
 Technology4 months ago
What Is Fanquer? The Digital Creator Platform Transforming Direct-to-Fan Engagement
-
 Celebrity3 months ago
Dr Jared Ross: Missouri Appeals Court Upholds Protection Order Over Graphic Torture and Murder Threats
-
Celebrity10 months ago
Nancy Hallam: The Inspiring Life, Career, and Success Story Behind Ian Wright’s Wife
-
 Health8 months ago
Enclomimed 25 (Enclomiphene) – Effective PCT Protocol
-
 Celebrity10 months ago
Who Is Maisie Mae Roffey? The Private Life, Family Story, and Quiet Success of Julie Walters’ Daughter