Tech
Account Safety 101: How to Vet Any Instagram Growth Service

An Instagram growth service is not simply a purchase of more followers. It is a supplier decision that may involve account permissions, customer data, payment details and public-facing advertising. That makes the first question less “How quickly can it grow my account?” and more “What exactly will it do, and what access does it need to do it?”
A credible provider should be able to answer that plainly, in writing, before payment. If it cannot, the promised result is beside the point.
First, identify what is actually being sold
The service label matters less than the provider’s method, access requirements and ability to document the work.
“Growth” is used for several very different services:
- Social media management: planning content, publishing approved posts, handling comments and reporting on results.
- Strategy and analytics: audience research, profile improvements, content testing and measurement.
- Paid advertising: buying exposure through Meta’s advertising tools, with defined targeting, budget and campaign objectives.
- Creator or partnership outreach: identifying relevant collaborators and managing legitimate campaign activity.
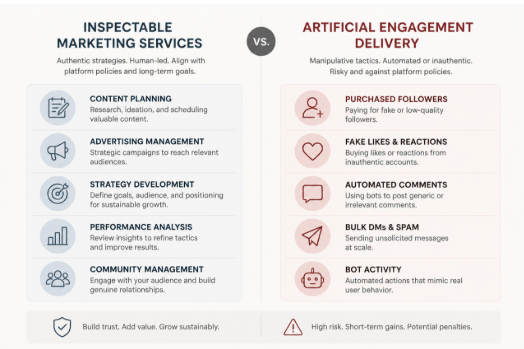
- Artificial follower or engagement delivery: supplying followers, likes, comments, views or automated actions intended to make an account appear more popular.
The first four can be legitimate marketing services, though quality varies. The last category deserves much closer scrutiny. Meta has publicly acted against services that used bots or automation to inflate likes, followers, views and comments; its account of action against fake engagement and ad scams is a useful reminder that artificial activity conflicts with its policies.
That does not mean every provider using the word “growth” operates in the same way. It means terms such as “organic”, “targeted”, “real users” and “human-led” are claims to investigate, not proof of a method. Ask what actions are performed, by whom, on which accounts, and how the provider avoids artificial engagement.
For a separate explanation of the trade-offs around artificial audience delivery, see Brecktic’s guide to whether buying Instagram followers is safe. The practical issue is not merely whether a number rises; it is whether the activity is authentic, relevant and safe for the account.
The non-negotiable rule: do not hand over credentials
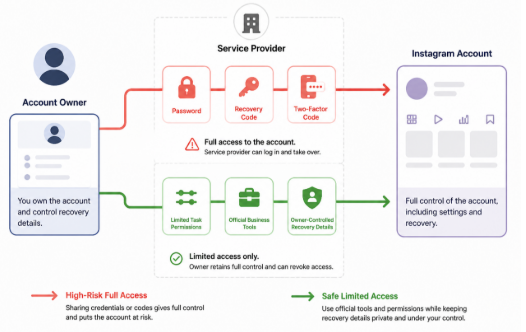
Safer onboarding limits permissions to the defined task and keeps authentication and recovery controls with the account owner.
Do not provide an Instagram password, recovery code, login code or two-factor authentication code to a growth provider. These are authentication secrets, not routine onboarding information. A request for them is a major security warning, even if the website appears polished or the provider says access is needed to “set up” the service.
Meta specifically advises people not to give Facebook or Instagram passwords to third-party sites or apps offering followers, likes or similar services outside official login mechanisms. A password can enable a third party to change recovery details, approve new sessions or lock the account owner out. A one-time code can be equally consequential if it is used to approve a login.
A safer workflow minimises access:
- Give a contractor only the role or task access needed for a defined job, where Meta’s current tools support it.
- Use official business or advertising tools for paid campaigns rather than sharing a personal login.
- Treat connected apps as permissions, not harmless add-ons. Check what an app can read, publish or manage before authorising it.
- Keep the account owner’s email address, phone number and recovery options under the owner’s control.
- Enable two-step verification. The UK National Cyber Security Centre recommends it for important accounts because it adds a further check if a password is stolen.
Permission names and menus change, so confirm the live settings in Meta’s help documentation before assigning access. The governing principle does not change: give the least privilege necessary, for the shortest practical period.
Red flags: stop signs versus questions to investigate
A useful vetting process separates reasons to walk away from issues that need clarification.
Stop signs
Leave the checkout process if a provider:
- asks for a password, recovery information or authentication code;
- promises a guaranteed volume of followers, likes or comments on a fixed timetable without explaining the source;
- offers immediate delivery of large quantities of engagement;
- cannot say whether bots, automated actions, engagement pods or follow-unfollow tactics are involved;
- uses urgency to push payment before terms can be reviewed;
- has no identifiable business, working support route, privacy information or commercial terms; or
- directs payment to an unrelated individual or asks for an unusually hard-to-reverse payment method.
None of these signals alone proves criminal intent. Together, they point to an unacceptable combination of security, supplier and reputational risk.
Caution signs
Pause and ask more questions when a provider:
- calls its service “organic” but provides no operational explanation;
- shows only follower-count screenshots rather than methodology or meaningful outcomes;
- makes broad claims about algorithm access, insider knowledge or guaranteed reach;
- will not define cancellation, refunds, renewal or notice periods;
- cannot explain how it handles client contact details and account data; or
- presents testimonials but no verifiable business identity or independent reputation trail.
The important distinction is between a provider that can document its process and one that substitutes slogans for evidence.
Run a five-minute website and checkout audit
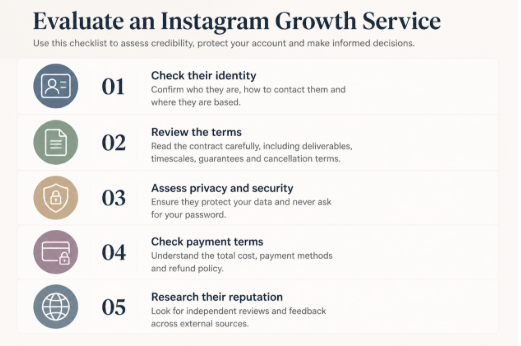
A quick supplier audit can expose unclear identity, access demands and weak commercial terms before payment.
Before paying, perform a basic supplier check. This is not a formal certification process; it is a quick way to decide whether the provider merits further discussion.
1. Check identity. Look for a legal business name, a physical or registered contact route, a company number where applicable, and a domain-based support address. For UK customers, compare company details with the public Companies House register where a company number is supplied. A brand name alone is not enough to establish who will hold your payment or data.
2. Read the commercial terms. Find the total price, billing frequency, cancellation process, refund conditions, delivery description and complaint route. Vague wording such as “results may vary” does not replace a clear explanation of what is being purchased.
3. Inspect data handling. A privacy notice should say what information is collected, why it is used and how to contact the organisation. Be especially wary if a supplier requests more account data than its stated service requires.
4. Check the payment path. Confirm that the checkout domain, merchant description and business identity are consistent. Prefer a payment route that offers a record of the transaction and a defined dispute process. Do not confuse a padlock icon with proof that a business is trustworthy; it only indicates a protected connection.
5. Search beyond the provider’s own site. Look for a durable trail: business listings, editorial mentions, support responsiveness and reviews that discuss specific work rather than repeating generic praise. Treat reviews as one input, not conclusive proof.
Test the delivery model, not the marketing language
Ask prospective providers these questions in writing:
- What actions will you take on my behalf?
- Will any action be automated? If so, which action and with what safeguards?
- Where does the prospective audience come from, and how is relevance to my UK market assessed?
- Are followers, likes or comments purchased, incentivised, exchanged or otherwise artificially delivered?
- What account access is required, and why is each permission necessary?
- What is the smallest paid test, and how can I end it?
A strong answer describes a process: content work, campaign setup, audience research, outreach, ad spend management or reporting. A weak answer circles back to a result: “real growth”, “premium followers” or “safe engagement”.
Be particularly careful with “guaranteed” results. Marketing can set service levels, such as a reporting schedule or number of approved posts. It cannot credibly guarantee that a particular number of people will become genuinely interested in a business on demand.
Measure outcomes that matter
Follower totals are easy to display but weak evidence of commercial value on their own. They do not show whether new people are relevant to the business, remain engaged, visit a website, enquire, buy or remember the brand.
Ask for reporting that distinguishes activity from outcome. Depending on the objective, useful reporting may include:
- the audience and geography the work was intended to reach;
- content themes and creative tests undertaken;
- reach and meaningful interactions over a stated period;
- profile visits, link actions, enquiries or sales where tracking is available;
- paid-media spend separated from agency fees;
- source data from the platform, not just a designed summary; and
- lessons, limitations and the next test.
No single metric proves success. A good report explains what happened, how it was measured and what decision follows. It should also make it possible to spot a mismatch between a rising follower count and an audience that has little reason to care about the account.
UK advertising: keep commercial content identifiable
Growth work can overlap with influencer marketing, gifted activity and paid collaborations. Where content is advertising, UK guidance expects it to be obviously identifiable. The ASA and CAP’s guidance on recognising ads in social media and influencer marketing explains that labels such as “Ad” should be clear and prominent, generally before people need to engage with the content.
Responsibility can extend to brands, agencies and influencers. The exact position depends on the relationship and content, so this is general information rather than legal advice. Build disclosure review into campaign approval instead of treating it as a last-minute caption edit.
A simple scorecard for any provider
Use this editorial scorecard before proceeding:
| Area | Pass | Caution | Stop |
| — | — | — | — |
| Identity | Verifiable business and responsive contact route | Limited history or incomplete details | No accountable identity |
| Access | Least-privilege permissions, no credentials | Access explanation is unclear | Requests password or codes |
| Method | Specific, documented process | Vague claims need answers | Artificial delivery or undisclosed automation |
| Terms | Clear price, scope and exit route | Ambiguous clauses | Hidden renewal or no cancellation route |
| Reporting | Objectives, source data and learning | Follower-led reporting | Only promises and screenshots |
| Testability | Small, reversible trial | Large minimum commitment | Pressure for a major upfront payment |
One stop result should end the conversation. Caution results are not an automatic rejection, but they should be resolved in writing before money or permissions change hands.
If you have already shared access
Act promptly. Change the Instagram password from a trusted device, turn on two-step verification, and review account contact and recovery details. Check active sessions and connected apps, remove anything unfamiliar, and review any business or advertising access that you do not recognise. Monitor recent posts, messages, profile edits and payment activity.
If you can no longer access the account, use Instagram’s official recovery route. Retaining control of the linked email address and phone number can be important to recovery, so secure those accounts too. If payment details were shared, contact the payment provider promptly and preserve relevant records, including receipts, emails and screenshots.
Choose growth mechanisms you can inspect
The lowest-risk options are generally the ones a client can see and evaluate: stronger content planning, a clear profile proposition, legitimate collaborations, responsive community management and advertising run through official tools with defined objectives and budgets.
A provider does not need to promise artificial popularity to be useful. It should explain its method, restrict access, document the commercial relationship and report on outcomes relevant to the business. For further reading on account-safety considerations, Brecktic provides additional context.
The core test is simple: if a service cannot explain how it works without asking you to trust a vague promise or surrender control of the account, it is not ready to be hired.
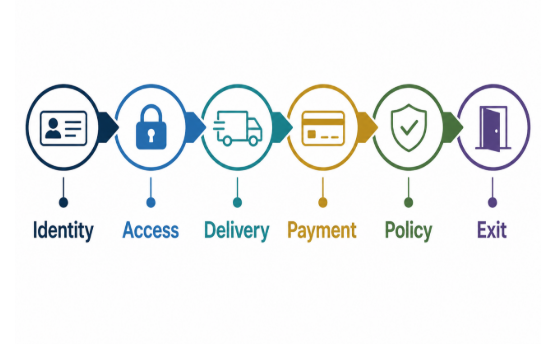
A practical six-control framework for assessing an Instagram growth service before granting access or paying.
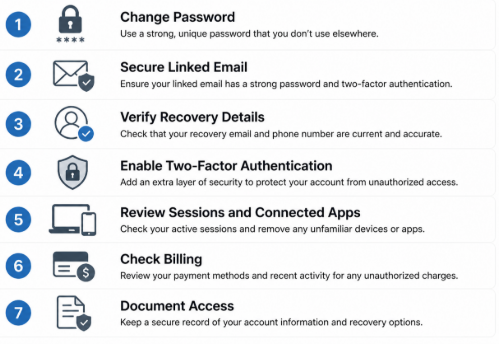
Immediate account-security checks after sharing access with an external provider.
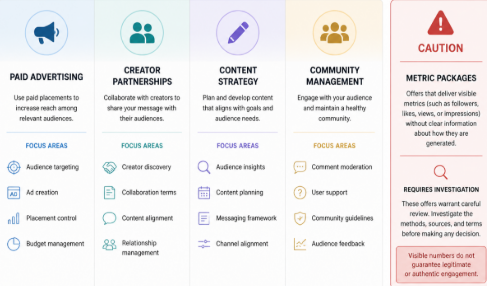
Different service models require different checks; a headline metric does not explain how activity is generated.



Business communication has changed dramatically over the past decade. Teams no longer depend entirely on desk phones, physical offices, or traditional telephone networks to stay connected. Employees work from different cities, customer support teams operate across time zones, and businesses increasingly expect communication tools to work alongside the digital applications they already use. In this environment, VoIP technology has become an important part of how modern organizations handle voice communication.
Voice over Internet Protocol, commonly known as VoIP, allows voice calls to travel over internet networks rather than traditional telephone infrastructure. That simple change opens the door to a much more flexible communication environment. Businesses can connect employees, customers, sales teams, support agents, and distributed teams through software-based phone systems accessible from computers, smartphones, IP phones, and other connected devices.
But VoIP is not simply about making cheaper phone calls. Modern VoIP solutions can include call routing, interactive voice response, call recording, analytics, conferencing, voicemail, CRM integration, mobile access, and automation. In other words, the business phone system is becoming less like a standalone appliance and more like a connected software platform.
What Is VoIP Technology and How Does It Work?
VoIP technology converts voice conversations into digital data and transmits that information through an internet connection. Instead of depending on a dedicated traditional telephone line for every conversation, VoIP systems use IP networks to establish and manage calls.
A typical business VoIP environment may include cloud infrastructure, SIP services, IP phones, computers, mobile applications, call management software, and business integrations. When these components are designed properly, employees can communicate through a unified system, whether they are working from an office, home, or another location.
- How VoIP Works
When a person speaks during a VoIP call, the system converts the audio into digital data packets. These packets travel through an IP network and are reconstructed as audio at the receiving end, allowing the conversation to happen in real time.
The process sounds technical, but the user experience can be remarkably simple. An employee can open a VoIP application, select a contact, and make a call much like they would with a conventional phone.
- VoIP vs Traditional Phone Systems
Traditional phone systems often depend on physical infrastructure, fixed lines, and hardware installed at specific locations. VoIP shifts much of that communication infrastructure into software and internet-based services.
This makes VoIP particularly useful for organizations that need flexibility. Instead of treating every new employee or office location as a major telephone infrastructure project, businesses can configure users and extensions through a software-based communication system.
You may also like: Top 10 VoIP Billing Solutions for Modern Businesses
Why VoIP Is Becoming Important for Modern Businesses
Modern companies need communication systems that can keep up with changing work patterns. Employees may move between offices, work remotely, travel frequently, or communicate with customers from mobile devices. A communication platform that is tied too closely to a physical location can become difficult to manage as the organization grows.
VoIP addresses this challenge by separating business communication from a specific physical phone line. Users can often access business calling features through compatible devices and applications, giving organizations greater flexibility in how they structure their communication workflows.
- Flexible and Remote Communication
One of the most useful aspects of VoIP is its support for distributed teams. Employees can use business communication tools from different locations while remaining connected to the organization’s phone system.
A sales representative working from home, a support agent in another city, and an employee working from the company office can all operate within the same communication environment. This flexibility is especially useful for businesses with hybrid and remote work models.
- Cost-Effective Business Calling
VoIP can also help businesses manage communication expenses by using internet connectivity instead of relying entirely on traditional telephone infrastructure. The overall cost depends on factors such as provider plans, call volume, features, infrastructure, and implementation requirements.
For businesses with multiple locations or significant calling requirements, consolidating communication through a VoIP platform can simplify management while potentially reducing certain telecommunication expenses.
Key Features of Modern VoIP Solutions
Modern business phone systems can do much more than connect two people on a voice call. VoIP platforms can combine calling, messaging, conferencing, call management, analytics, and integrations into a single communication environment.
This makes VoIP particularly valuable when communication needs to connect with broader business workflows. For example, a customer call can be associated with a CRM record, while a support interaction can be recorded and analyzed for quality management.
- Call Routing and IVR
Call routing and Interactive Voice Response (IVR) help businesses direct incoming calls to the right department or employee. Customers can select options from an automated menu, while routing rules can determine where calls should go based on business hours, availability, department, or other conditions.
A well-designed IVR system can reduce unnecessary transfers and help customers reach the appropriate team more efficiently. It can also provide basic information automatically without requiring an employee to handle every request.
- Call Recording and Analytics
Call recording can help businesses review conversations, train employees, maintain quality standards, and understand customer interactions. Depending on the system and applicable requirements, businesses can configure recording policies around specific users, departments, or call types.
VoIP analytics can provide additional visibility into communication activity. Metrics such as call volume, duration, missed calls, wait times, and agent activity can help managers understand how communication processes are performing.
- Video Calling and Team Collaboration
Many modern VoIP platforms extend beyond voice communication to include video meetings, conferencing, screen sharing, messaging, and collaboration features. This allows organizations to bring multiple communication methods into a connected environment.
Instead of switching between several unrelated applications, teams may be able to manage different forms of communication through a unified platform. That can simplify daily workflows, particularly for distributed teams.
Benefits of VoIP for Business Communication
The biggest advantage of VoIP is the flexibility it brings to business communication. Organizations can configure users, extensions, call flows, applications, and integrations according to their operational needs.
VoIP can also make it easier to connect with other digital systems. This is important because business conversations rarely happen in isolation. A customer call may involve a CRM record, a support ticket, an order, a sales opportunity, or a previous interaction.
- Easy Scalability
Traditional phone infrastructure can become complicated when a business adds employees, departments, or locations. VoIP systems can often make expansion more straightforward because users and extensions can be managed through software.
A growing company can add new employees, configure extensions, modify call routing, and introduce new communication features without necessarily redesigning its entire telephone infrastructure.
- Business Application Integration
VoIP can integrate with CRM, help desk, ERP, collaboration, and other business applications. With the right integration, employees can make calls directly from business software, access customer information during conversations, or automatically associate call activity with customer records.
This creates a more connected workflow. Instead of communication data remaining inside the phone system, it can become part of the broader digital customer and business experience.
How Businesses Are Using VoIP Technology
Businesses use VoIP across many functions because voice communication remains important as digital channels continue to expand. Sales teams use calls to communicate with prospects, support teams handle customer issues, and internal teams use voice and video for collaboration.
The technology is especially useful when organizations need communication across multiple locations while maintaining centralized control over users, call flows, and business numbers.
Customer Support and Call Centers
Customer service operations can use VoIP features such as IVR, call queues, call recording, agent routing, monitoring, and analytics. These capabilities help organizations structure large volumes of incoming and outgoing communication.
Call center managers can also use reporting features to understand call patterns and identify areas where customer communication processes may need adjustment.
Remote Teams and Distributed Workforces
VoIP makes it easier for remote employees to remain connected to the same business communication environment as office-based employees. Users can access calling features through supported desktop applications, mobile applications, or IP devices.
This can help businesses maintain consistent communication practices even when employees are distributed across different locations.
VoIP Security and Reliability Considerations
Because VoIP communication travels through digital networks, security must be an essential part of system design. Businesses should consider authentication, encryption, access controls, network security, fraud prevention, software updates, and monitoring when deploying a VoIP environment.
Reliability is equally important. Voice communication depends on network performance, bandwidth, latency, and system availability. Businesses should therefore evaluate their network infrastructure and consider appropriate redundancy, monitoring, backup connectivity, and disaster recovery strategies.
A reliable VoIP solution is not simply one that works when everything is normal. It should also have a plan for handling network disruptions, hardware failures, service interruptions, and unexpected traffic.
Challenges of Implementing VoIP
VoIP offers significant flexibility, but implementation still requires careful planning. Poor network quality can affect call performance, while incorrectly configured systems may create security or routing problems. Businesses also need to consider how the new communication platform will interact with existing applications and workflows.
Another challenge is user adoption. Employees need to understand how to use new calling features, applications, voicemail systems, conferencing tools, and collaboration capabilities. Proper configuration, testing, training, and ongoing support can make the transition much smoother.
For organizations with complex requirements, custom development may also be necessary. A business might need specialized call routing, custom dashboards, CRM integration, mobile applications, APIs, or unique automation workflows that are not available in an off-the-shelf platform.
How Moon Technolabs Can Help With VoIP Development
Moon Technolabs can help businesses develop custom VoIP solutions around their communication requirements. This can include VoIP application development, SIP integration, call management, IVR, call routing, conferencing, CRM integration, mobile communication, analytics, and other business communication capabilities.
The development approach can be tailored to the organization’s existing infrastructure and future growth plans. From designing the communication architecture to developing, integrating, testing, and maintaining the solution, a custom approach can help businesses create a VoIP environment that fits their workflows rather than forcing those workflows into a rigid communication platform.
Conclusion
VoIP technology is changing business communication by making voice services more flexible, software-driven, and connected. Businesses can move beyond traditional phone systems and introduce features such as intelligent call routing, IVR, analytics, recording, conferencing, mobile access, and business application integrations.
The real value of VoIP comes from how these features work together. A business can connect its phone system to customer data, support workflows, remote teams, and operational tools, making communication a more integrated part of the digital business environment.
As organizations continue adopting flexible and distributed working models, communication technology needs to support people wherever they work. VoIP provides a foundation for that while giving businesses greater control over how they manage, monitor, integrate, and scale calls.

Introduction
While RAID systems are designed for speed, redundancy and peace of mind, when they fail, the consequences can be much more complicated than just a single hard drive failure.
A basic recovery solution is just not going to do the job due to multiple disks, striped or mirrored data, and controller-level configurations.
This is where a Professional RAID Data Recovery Company in the UK begins to be of great help. Whether it’s a small studio or a national company, RAID arrays are vital to the smooth functioning of business operations, and an hour of downtime represents an hour of lost revenue, missed deadlines, and increased stress.
In a RAID 5 setup, if your array has degraded, in a RAID 0 setup if the stripe is corrupted, or in a RAID 6 setup if the RAID 6 controller fails, a skilled solution is the key to recovering all data and preventing data loss.
Let’s start by talking about the reasons why RAID failures are different:
The difference between a single drive failure and a RAID failure is that RAID failures are dependent on each other.
Data is not stored in a linear fashion on one disk, but rather is divided, striped, mirrored or parity-checked across multiple disks based on the RAID level used. This means that:
- If one drive fails in a RAID 0 array, all data is lost because there is no redundancy.
- RAID 5 and RAID 6 arrays are based on parity data, and when more drives fail than the array can handle, rebuilding is very complex.
- Even the steps of rebuilding the array can cause a logical disorder if the controller malfunctions, is corrupted by a virus or other software, or if it is incorrectly rebuilt.
- Recovery can be much more difficult as a result of human error, like trying to rebuild yourself or install drives in the wrong order.
The layers are exactly that these are the reasons why in general recovery software or even an unskilled technician might cause more harm than good.
A special team is aware of the RAID controller logic, stripe size and parity algorithms necessary to prevent the array from being reconstructed safely.
What Sets a Professional RAID Recovery Service Apart
A UK Professional RAID Data Recovery Company is a company that employs engineers who have successfully recovered thousands of real-world RAID failures on all of the most common RAID configurations from RAID 0 to RAID 10, as well as proprietary NAS and SAN systems from Synology, QNAP, Dell, HP, and others.
These are some of the benefits of having real RAID experts:
- Cleanroom Facilities: Physical drive failure (Clicking, Spindle damage, Head crashes) .Dust free environment needed to prevent further drive damage during disassembly.
- Instead of working on the live drives, engineers develop images, sector by sector, to preserve the original data while virtually reconstructing the array using Custom Imaging Tools.
- Deep Controller Knowledge: All RAID controllers have their own unique metadata. The correct stripe order, block size and rotation pattern can only be recovered with the help of reverse engineering. This is a process and does not involve just any software.
- No-Data, No-Fee Policies: reputable providers will not charge if the recovery is unsuccessful, meaning that the client will not be at any financial risk.
Businesses with sensitive or regulated data should expect providers to adhere to strict data protection protocols during recovery.Businesses with sensitive or regulated data should expect that providers will adhere to strict data protection protocols during the recovery.
The following is a list of basic RAID failure scenarios that we solve for you.
While there are many possible ways that RAID can fail, some of the most common are:
- Multiple Simultaneous Drive Failures: Two or more drives failing near each other, more than the array’s fault tolerance.
- Failed RAID Rebuilds: A rebuild that failed or was started by the incorrect order, typically making the problem worse before it gets better.
- Corrupted File Systems: The array is physically OK, but the file system (NTFS, EXT4, XFS, etc.) on top of it is corrupted.
- NAS and Server Crashes: Power surges, firmware bugs, or overheating and the entire storage server crashes.
- Accidental Reconfiguration: drives that have been reformatted, reinitialised or assigned to the wrong RAID level.
In all three, time and technique are crucial. If you continue to use a failed array or try to fix it any further without the proper expertise. The chances of recovering are much lower.
The Recovery Process: What to expect?
Usually, there is a structured and professional process that takes place:
- Initial Consultation: Provide information about symptoms, RAID level and recent events – such as rebuilds, power loss, drive replacement, etc. – to provide context for urgency and likely causes.
- Diagnostic Evaluation: Drives are checked one by one, and in array, for physical, logical or controller problems.
- Imaging: all drives are individually imaged to maintain the integrity of their data and to prevent additional wear.
- Virtual Array Reconstruction: In this case, engineers use the images to digitally reconstruct the RAID array (without any special software, and without correcting for stripe order, offset, and parity).
- Data Extraction and Verification: Extracted data, then integrity and delivery of organised recovered files.
- Secure Delivery: Data is transferred back through encrypted drives or secure transfer as per client’s wishes.
This is a systematic process that differentiates a Professional RAID Data Recovery Company in the UK from “standard” IT support and off-the-shelf RAID data recovery software, which can potentially overwrite recoverable information if improperly run on a failed RAID array.
The importance of acting promptly.
Once a RAID array sounds strange, has lost drives, performance has dropped or shares are unavailable, the best thing to do is to power it down and halt all data access to the RAID array.
The more an array is used, the more opportunity to over-write any recoverable sectors, particularly in arrays already running in a degraded state. Rather than trying to fix the house oneself, contacting a specialist as soon as possible maximizes the chances of a full and accurate recovery.
Conclusion
Failure of a RAID can never be a trivial matter, and always involves a substantial amount of data, from a small business’s customer information, to a media company’s archive or an enterprise’s operational database.
Many complex, multi-drive failures can be solved if the right people, tools, cleanroom facilities are available, but if not, it can become a permanent loss of data.
When you hire the services of an established and reputable RAID Data Recovery Company in the UK, you can rest assured that your data will be managed with the utmost technical precision, care, and confidentiality.
Expert engineers take you through the experience from diagnosis to secure delivery, so you can enjoy the best possible result, even with the most complicated RAID failures.

Payment service providers need a transaction monitoring platform that can hold up under high, uneven transaction volume without slowing settlement, give compliance teams direct control over rules and scenarios, and produce alerts and investigations that stay defensible as volume grows. Flagright’s real-time monitoring, no-code rule and scenario configuration, AI-assisted investigation workflow, and explainability architecture are built around this exact combination. This guide breaks down the specific risk and scaling pressures PSPs face and evaluates what to look for in monitoring speed, rule configurability, alert quality, investigation workflow, and explainability.
Why PSPs Face a Different Monitoring Problem Than Banks
Payment service providers sit in a structurally different position than a bank or a single-product fintech. A PSP typically processes transactions across multiple products at once, card processing, open banking rails, bank transfers, digital wallets, and payout orchestration, often for many underlying merchants or platform customers rather than a single retail customer base. Volume is uneven by nature: a PSP’s transaction count can spike sharply around a merchant’s promotional event, a payout cycle, or a seasonal surge, with no advance warning to the compliance team.
This creates three specific pressures that a generic AML buying checklist does not capture well.
Volume without margin for delay. PSPs operate on thin per-transaction margins at high volume, so a monitoring system that adds latency to the payment flow is not just an inconvenience, it is a direct cost. Monitoring has to happen at the speed of the transaction, not after it.
Alert volume that scales faster than headcount. As a PSP’s merchant base and transaction count grow, alert volume from a poorly tuned system grows with it, often faster than the compliance team can hire. Rules-based systems generic across industries frequently produce false-positive rates over 90%, and for a PSP running that ratio at high transaction volume, the resulting queue overwhelms any reasonably staffed team.
Explainability that satisfies more than one audience. A PSP’s monitoring decisions get scrutinized by bank regulators, but also by card networks, sponsor banks, and sometimes acquiring partners conducting their own due diligence. “The model flagged it” is not sufficient in any of these reviews. Every alert disposition needs a reasoning chain that a non-technical reviewer can follow.
What to Evaluate: Monitoring Speed
Real-time detection is now the baseline expectation for a PSP, not a differentiator, because payment rails increasingly settle in seconds and there is no batch window to catch problems after the fact. Flagright reports sub-second API response times maintained during peak transaction volume, positioned specifically for payment gateways and PSPs handling large transaction volumes under regulatory scrutiny. Industry-wide framing from ComplyAdvantage’s own PSP-focused guidance echoes this same requirement, describing infrastructure that needs to scale to millions of transactions per second so that compliance monitoring never becomes the bottleneck in the payment flow. When evaluating a vendor, ask for documented response-time figures under the specific transaction volume your business runs, not just an average across all customers.
What to Evaluate: Rules and Scenario Configuration
For a PSP running multiple products and merchant types, rule configuration needs to happen fast and without a permanent engineering dependency, because new fraud patterns and new merchant categories appear faster than a development sprint cycle allows.
➡️ Pre-built scenario libraries matter more for PSPs than for single-product businesses. Flagright ships over 100 pre-configured, typology-tagged scenarios covering structuring, rapid fund layering, high-risk geography flags, dormancy-triggered activity spikes, and cross-border anomalies, letting a PSP activate meaningful coverage immediately rather than starting from a blank rule canvas for every product line it monitors.
➡️ No-code configuration removes the engineering bottleneck. Flagright’s rule builder lets a compliance team describe a pattern in natural language, which pre-fills rule logic that the team can adjust and deploy without an engineer at any step. One Flagright customer described implementing new detection rules in minutes instead of weeks. Unit21 offers a comparable no-code rule builder with customizable variables, and G2 reviewers specifically credit its ability to create custom rules and its shadow-mode testing capability, so this is a genuinely contested area between the two platforms rather than a clear Flagright advantage.
➡️ Testing before deployment reduces the risk of a bad rule reaching production. Flagright’s workflow includes backtesting a new rule against 90 days of historical transactions to see projected alert volume and false-positive rate before it goes live, followed by an optional shadow-mode period where the rule runs against live transactions without generating analyst-facing alerts, so performance can be validated with zero disruption before go-live.
What to Evaluate: Alert Quality
Alert quality, not raw detection sensitivity, is usually the deciding factor for a PSP’s day-to-day operations, because a system that flags everything is functionally the same as a system that flags nothing useful. Flagright’s platform includes rule-performance analytics that flag both under-triggering rules, a red flag if a known typology in your business never generates an alert, and over-triggering rules, where a sudden spike may indicate either an emerging trend or a misconfiguration. The system’s recommendations draw on transaction data trends, historical alert-to-SAR conversion rates, and industry-wide patterns observed across its client base, aimed at keeping alert volume proportional to actual risk as a PSP scales rather than proportional to raw transaction count.
What to Evaluate: Investigation Workflow
For a PSP with a growing alert queue, how efficiently an alert becomes a resolved, documented case determines whether compliance headcount can keep pace with volume growth.
Flagright’s AI Forensics operates natively inside case management, beginning an investigation automatically with evidence, typology matches, and a recommendation before an analyst even opens the case. One named customer, Ieva Staskeviciute, Head of Financial Crime Monitoring, credited the case management workflow with giving clear visibility over actions taken, supporting collaboration between team members, and maintaining a comprehensive audit trail. Flagright’s own materials cite investigations moving up to 90% faster with AI Forensics support, and a separate customer quote describes having nearly eliminated the time spent writing narratives manually, since the system generates them in seconds for analyst review. SAR narratives are generated from live case data and jurisdiction-appropriate templates, with the analyst reviewing and filing rather than drafting from scratch.
What to Evaluate: Explainability
Explainability is the criterion most likely to be treated as a checkbox rather than examined closely, and for a PSP facing scrutiny from regulators, card networks, and sponsor banks simultaneously, that is a mistake. Flagright’s architecture logs every action an AI agent takes, including data retrieved and analysis performed, directly into the case timeline, with any conclusion or risk score accompanied by supporting evidence. AI-generated narratives and recommendations are reviewable and editable by a human investigator before anything is finalized, keeping the ultimate decision under compliance team control. Flagright’s own public framing of this, from its CEO, argues that financial institutions need audit-ready infrastructure combining deterministic systems with generative AI, because every compliance decision must remain traceable and defensible to an examiner. ComplyAdvantage uses comparable language for the PSP segment specifically, describing a “glass box” approach where every decision carries an immutable, full-reasoning audit log, which suggests this bar is becoming standard across serious platforms in this space rather than a unique claim, and a PSP evaluating vendors should ask each one to demonstrate the actual audit trail on a real alert, not just describe the concept.
What to Evaluate: Integration and Scalability
A PSP’s monitoring platform has to sit across multiple payment rails and product types without requiring a separate integration effort for each one. Flagright’s evidence here includes B4B Payments, a payment processor case study describing improved fraud detection and AML monitoring capability alongside a structured onboarding process that included rule migration, enabling the compliance team to manage investigations confidently from the start. Flagright positions its platform as managing AML compliance and risk across card processing, open banking, bank transfers, digital wallets, and payout orchestration on one system, avoiding the fragmentation of running separate tools per product line. On the competitor side, Unit21 has been named a Category Leader in Chartis’s 2026 RiskTech Quadrant for both Enterprise Fraud Solutions and Payment Fraud Solutions, an independent analyst signal worth weighing, and ComplyAdvantage’s Mesh platform, launched in late 2025, unifies customer screening, risk scoring, transaction monitoring, and payment screening in one system, a genuinely comparable consolidation move.
Recommendation
For a PSP prioritizing scalability specifically, meaning the ability to absorb volume growth, new products, and new merchant categories without a monitoring re-platform, the deciding factors are speed under load, how much rule and scenario control sits with the compliance team rather than engineering, and whether the investigation and explainability layer can keep pace with a growing alert queue without proportional headcount growth. Flagright’s combination of sub-second response times, no-code scenario configuration with pre-built typology coverage, and AI Forensics investigation support addresses each of these directly, with the B4B Payments case study as PSP-specific evidence. Unit21 is a legitimate alternative where a PSP’s compliance team specifically values a longer-established no-code rule builder and independent analyst recognition for payment fraud specifically. ComplyAdvantage is worth evaluating where screening data depth and a newly unified Mesh platform matter more to a PSP than transaction monitoring configurability. Any PSP should request a demonstration using its own historical transaction volume and alert data rather than relying on vendor-published averages, since performance at scale is the actual question being answered.
Material Considerations
- Flagright cites uptime figures of both 99.99% and 99.998% in different materials; confirm the current figure directly with the vendor before relying on it in an SLA discussion.
- The 90% faster investigation and 93% false-positive reduction figures cited above are self-reported by Flagright without a publicly disclosed baseline or methodology; ask for the underlying calculation before using these numbers in an internal business case.
- Rules-based systems commonly cited as producing 90%+ false-positive rates is an industry-wide figure, not specific to any single vendor, and actual performance depends heavily on a PSP’s own configuration and tuning.
- Implementation timelines and rule-migration scope for PSPs specifically will vary by how many products and rails are in scope; confirm the scope behind any timeline a vendor quotes.
FAQ
Does a PSP need real-time monitoring, or is near real-time sufficient? This depends on the payment rails a PSP supports. Any rail that settles in seconds, such as instant transfers or many card transactions, effectively requires real-time monitoring, since there is no batch window afterward to catch a problem before funds move.
How many pre-built scenarios does a PSP actually need at launch? This varies by product mix, but a PSP running multiple products, such as card processing alongside bank transfers, typically needs broader scenario coverage than a single-product fintech. Look for a vendor with typology-tagged scenarios specific to each rail or product type you support, rather than one generic scenario set.
What is the difference between shadow-mode testing and backtesting a rule? Backtesting runs a new rule against historical transaction data to estimate what alert volume and false-positive rate it would have produced. Shadow mode runs the rule against live, current transactions without generating analyst-facing alerts, so its real-world performance can be validated before it affects the live queue.
How should a PSP evaluate a vendor’s explainability claims? Ask to see the actual audit trail behind a specific alert disposition during a demo, not just a description of the capability. A credible platform should be able to show what data was reviewed, what reasoning led to a conclusion, and where a human reviewed or adjusted that conclusion.
Can a PSP switch monitoring vendors without disrupting operations? It depends heavily on the migration support offered. Look for vendors with a documented rule-migration process and structured onboarding, since re-creating detection logic from scratch during a vendor switch is one of the more common sources of a coverage gap.

Account Safety 101: How to Vet Any Instagram Growth Service

What Makes Underground Streetwear Hit? Breaking Down the MF DOOM Shirt and Parke Hoodie Hype

Unlocking Peak Performance with AMD Ryzen X3D: A Gamer’s Ultimate Guide

5 questions every Sydney homeowner should ask before hiring a plumber

Transforming Business Efficiency with Modern Workplace Solutions

Empowering Success: Comprehensive NDIS Student Support Services

The 15 Highest-Paid Rugby Players in the World
Christopher Dare: The Untold Story of Engineer and Former Husband of Angela Rippon

How to Ensure Your Home is Valued Correctly for a Quick Sale

What Is Fanquer? The Digital Creator Platform Transforming Direct-to-Fan Engagement

Dr Jared Ross: Missouri Appeals Court Upholds Protection Order Over Graphic Torture and Murder Threats
Nancy Hallam: The Inspiring Life, Career, and Success Story Behind Ian Wright’s Wife
The 15 Highest-Paid Rugby Players in the World
Christopher Dare: The Untold Story of Engineer and Former Husband of Angela Rippon
How to Ensure Your Home is Valued Correctly for a Quick Sale
What Is Fanquer? The Digital Creator Platform Transforming Direct-to-Fan Engagement
Dr Jared Ross: Missouri Appeals Court Upholds Protection Order Over Graphic Torture and Murder Threats
Nancy Hallam: The Inspiring Life, Career, and Success Story Behind Ian Wright’s Wife
-
 Sports5 months ago
The 15 Highest-Paid Rugby Players in the World
-
Celebrity10 months ago
Christopher Dare: The Untold Story of Engineer and Former Husband of Angela Rippon
-
 Real Estate8 months ago
How to Ensure Your Home is Valued Correctly for a Quick Sale
-
 Technology4 months ago
What Is Fanquer? The Digital Creator Platform Transforming Direct-to-Fan Engagement
-
 Celebrity4 months ago
Dr Jared Ross: Missouri Appeals Court Upholds Protection Order Over Graphic Torture and Murder Threats
-
Celebrity11 months ago
Nancy Hallam: The Inspiring Life, Career, and Success Story Behind Ian Wright’s Wife
-
 Health9 months ago
Enclomimed 25 (Enclomiphene) – Effective PCT Protocol
-
 Celebrity11 months ago
Who Is Maisie Mae Roffey? The Private Life, Family Story, and Quiet Success of Julie Walters’ Daughter