Entertainment
What a Cloud Storage Risk Assessment Template Should Include According to NIST and ISO 27001 Standards

Organizations moving critical data to cloud storage environments face a consistent operational challenge: the gap between assuming a system is secure and being able to demonstrate it. Cloud providers offer infrastructure, redundancy, and availability guarantees, but those guarantees do not extend to how an organization configures its storage, controls access, or handles sensitive data classifications. That gap is where risk accumulates quietly, often undetected until a compliance audit, a data incident, or a vendor review surfaces the problem.
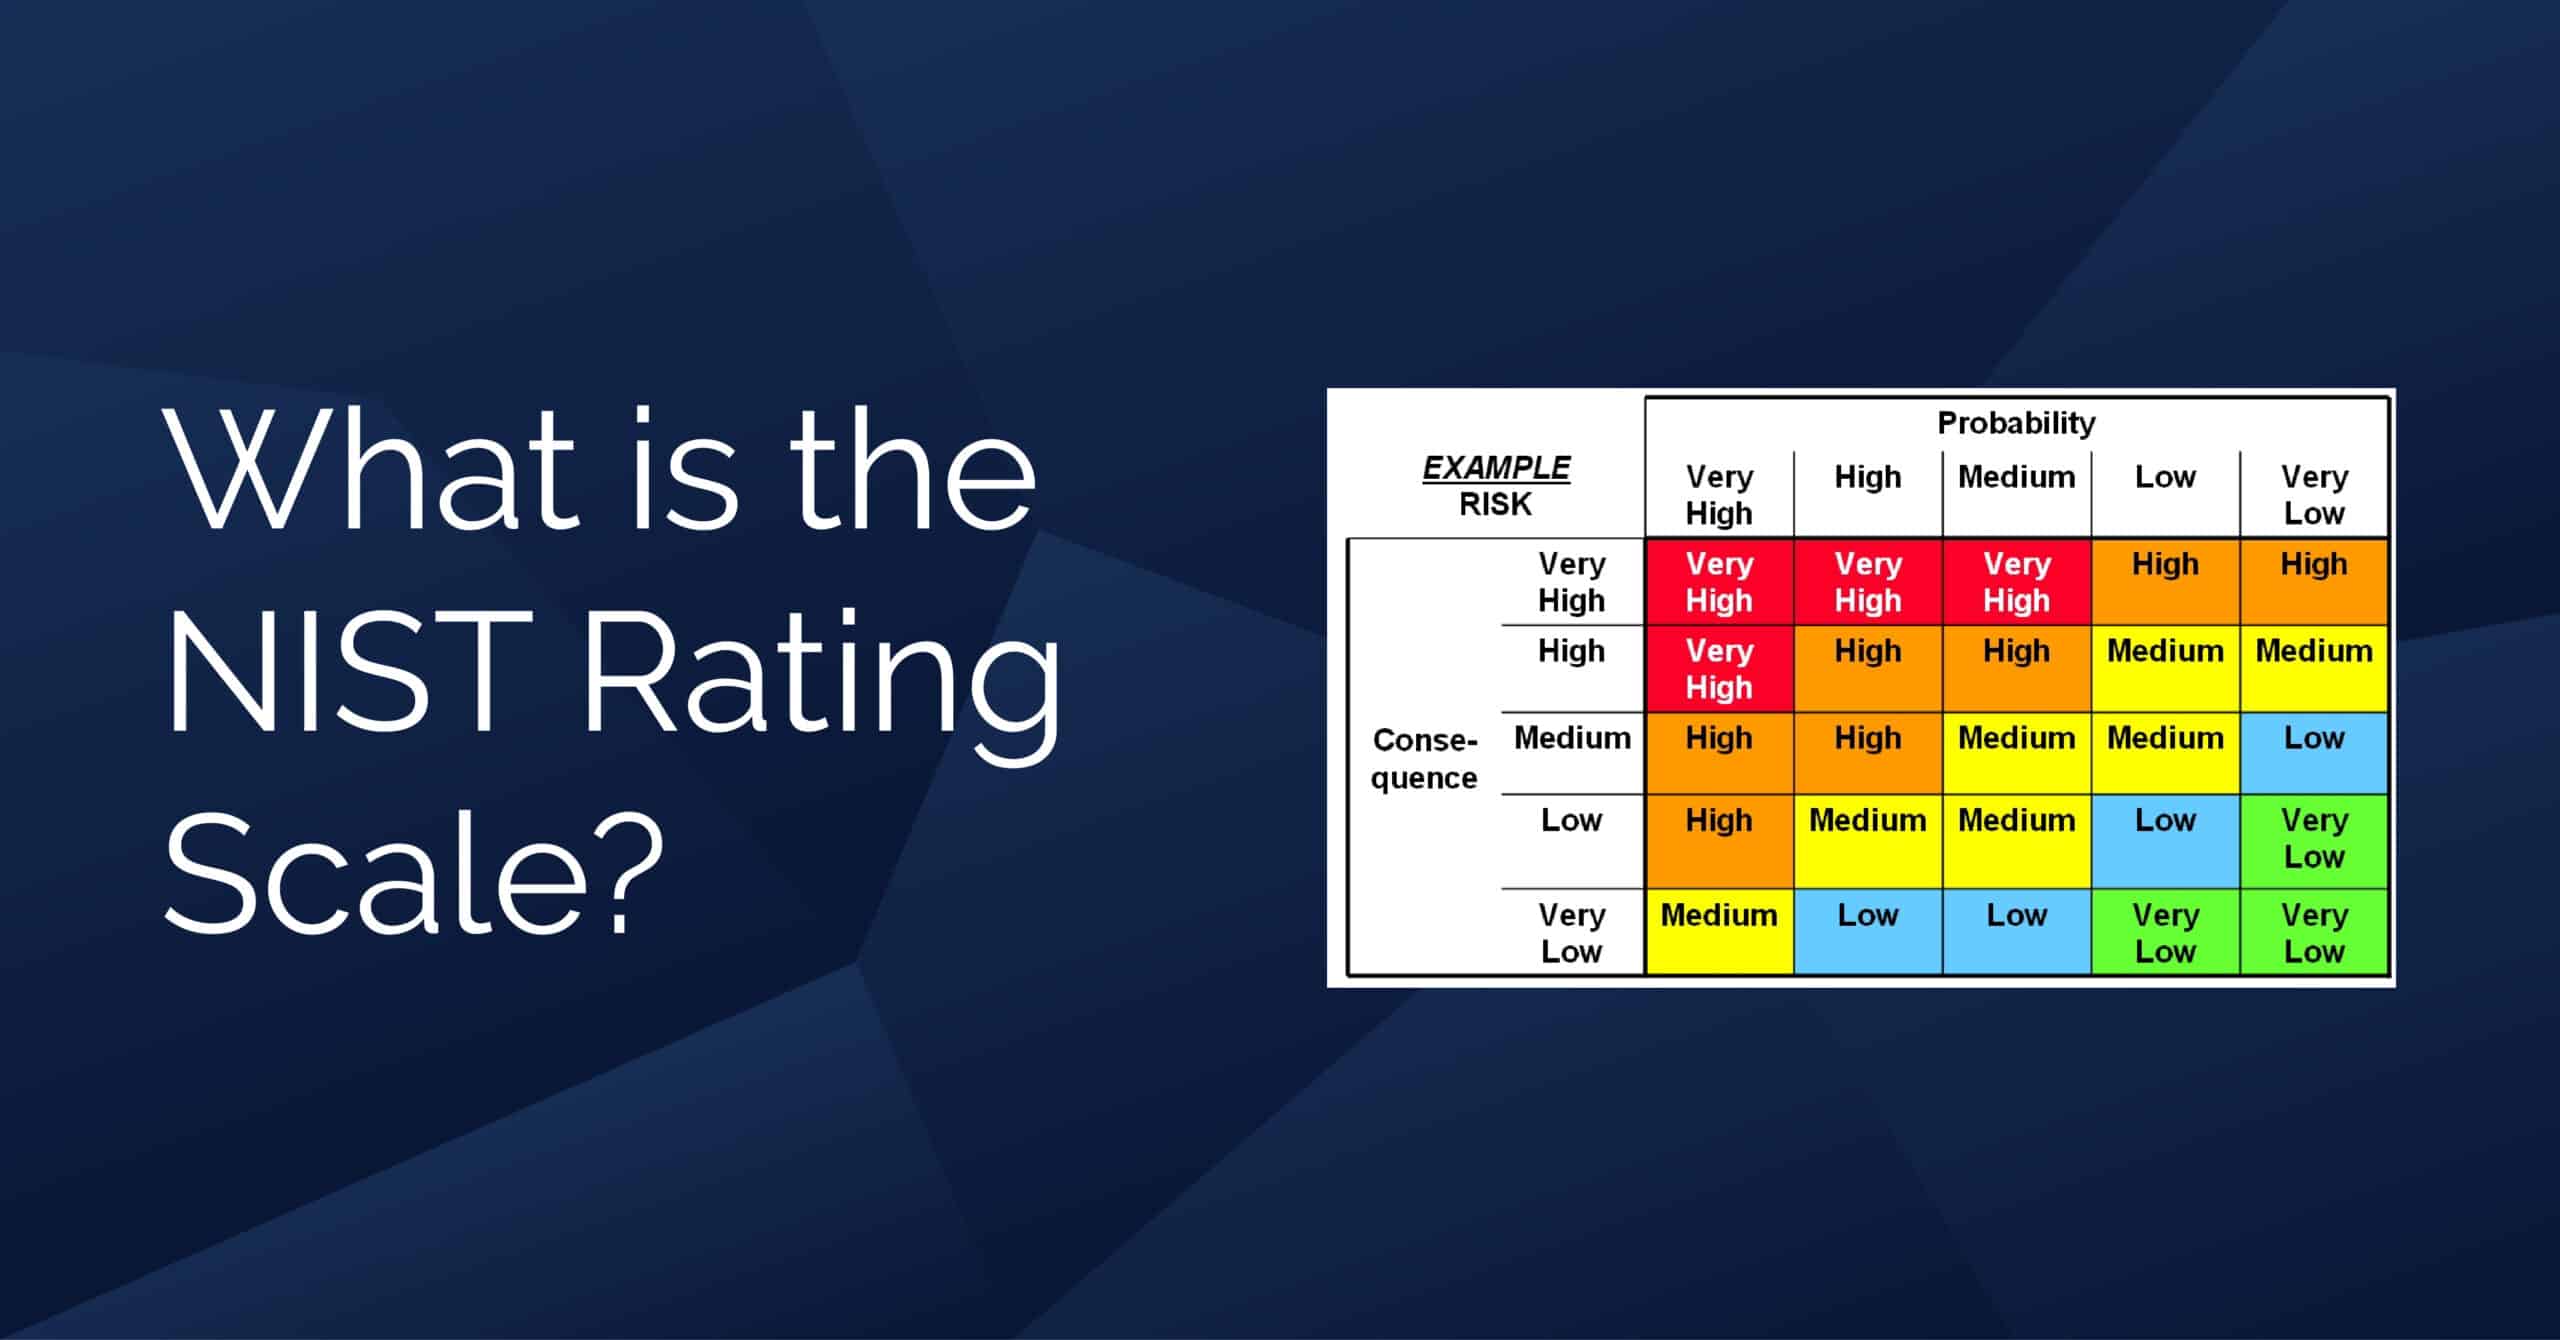
The need for a structured assessment process has grown alongside cloud adoption. As more organizations rely on cloud storage for operational continuity, financial records, client data, and regulated information, the absence of a defined risk review process creates real exposure. Regulatory frameworks including NIST and ISO 27001 have both addressed this by providing organizations with structured criteria for identifying and managing cloud storage risk. Understanding how those criteria translate into a practical assessment document is the first step toward closing the gap between assumption and evidence.
Why a Structured Template Matters for Cloud Storage Risk
A cloud storage risk assessment template gives organizations a repeatable, documented way to evaluate the security posture of their cloud storage environments against defined criteria. Without a template, assessments tend to be informal, inconsistent across teams, and difficult to audit. A well-constructed cloud storage risk assessment template anchors each evaluation to specific controls, expected outcomes, and accountability assignments, which matters significantly when demonstrating compliance to third parties or regulators.
The value of using a structured cloud storage risk assessment template is that it removes ambiguity from the process. Each evaluator works from the same criteria, measures the same control categories, and documents findings in a consistent format. This consistency becomes especially important when assessments need to be compared over time or reviewed across business units with different cloud configurations.
NIST and ISO 27001 both provide frameworks that organizations can use as the backbone of this kind of assessment. NIST’s Special Publication 800-53 and the Cloud Computing Security Reference Architecture define control families relevant to storage systems. ISO 27001 Annex A provides a set of information security controls that map directly onto cloud storage risk categories. Neither framework prescribes a specific template format, but both define the control areas that any credible assessment must address.
The Role of Control Mapping in Template Design
A cloud storage risk assessment that is not mapped to a recognized control framework is difficult to defend in a compliance context. Control mapping means that each section of the assessment corresponds to a specific requirement in NIST, ISO 27001, or both. When an evaluator identifies a risk in access control or encryption configuration, that finding is tied back to a defined control, which makes the remediation path clearer and the documentation more credible.
Control mapping also helps organizations avoid scope drift. Without explicit framework alignment, assessments often expand into tangential areas or miss critical categories entirely. The template structure itself enforces scope discipline by requiring the evaluator to address each control family systematically rather than selectively.
Data Classification and Asset Inventory as a Starting Point
Both NIST and ISO 27001 treat asset identification and data classification as foundational steps in any security assessment. For cloud storage specifically, this means the assessment must begin by identifying what data resides in each storage environment, how that data is classified in terms of sensitivity and regulatory relevance, and who is responsible for its protection. Without this inventory, subsequent risk evaluations have no reliable basis.
ISO 27001 Annex A.8 addresses information asset management directly, requiring organizations to identify assets, assign ownership, and apply appropriate classification labels. NIST’s categorization methodology, drawn from FIPS 199 and SP 800-60, provides a structured approach to determining the security category of information based on confidentiality, integrity, and availability requirements. A cloud storage risk assessment template should incorporate both of these approaches, with dedicated sections for asset listing, classification criteria, and ownership assignment.
Why Ownership Assignment Affects Risk Outcomes
One of the most common weaknesses in cloud storage risk programs is unclear ownership. When multiple teams share access to a cloud storage environment without a defined owner, accountability for access reviews, configuration changes, and incident response becomes fragmented. The template should require explicit ownership documentation for each storage bucket, container, or volume assessed, along with the owner’s responsibilities under the organization’s information security policy.
Ownership clarity also affects how findings are remediated. When a control gap is identified, the assigned owner is responsible for addressing it within a defined timeframe. Without that assignment documented in the assessment, findings tend to remain open indefinitely because no team has clear accountability for resolution.
Access Control and Identity Verification Requirements
Access control is consistently among the highest-risk areas in cloud storage environments. Misconfigured permissions, overly broad access policies, and unreviewed service accounts are among the most frequently cited causes of cloud data exposure. NIST SP 800-53 includes an extensive set of access control requirements under the AC family, covering account management, least privilege, session controls, and remote access. ISO 27001 Annex A.9 addresses access control across user registration, privilege management, and authentication requirements.
A cloud storage risk assessment template must include a section dedicated to evaluating how access is granted, reviewed, and revoked. This section should assess whether role-based access control is consistently applied, whether multi-factor authentication is enforced for administrative access, and whether inactive or orphaned accounts have been identified and removed. These are not aspirational practices — they are specific requirements under both NIST and ISO 27001 that assessors must verify against documented evidence.
Service Accounts and Automated Access Paths
Automated processes that read from or write to cloud storage often operate under service accounts that are granted broad permissions for convenience. These accounts present a distinct risk category because they are rarely subject to the same review cycles as human user accounts. A rigorous assessment template should include specific criteria for evaluating service account permissions, rotation schedules for associated credentials, and whether access logs for these accounts are being reviewed at defined intervals.
The NIST Cybersecurity Framework specifically addresses the need for identity and credential management as part of the Protect function, reinforcing that automated access paths require the same discipline as direct user access.
Encryption Standards and Data Protection Controls
Encryption requirements for cloud storage span two distinct states: data at rest and data in transit. Both NIST and ISO 27001 address these states with specific control expectations. NIST SP 800-111 provides guidance on storage encryption, and ISO 27001 Annex A.10 covers cryptography policy and key management. A cloud storage risk assessment template should evaluate both whether encryption is applied and whether the implementation meets the standards required for the data classification assigned to each storage asset.
Key management is a component of encryption assessment that is frequently underexamined. Encryption without proper key management controls introduces its own risk — if encryption keys are stored alongside the data they protect or if key rotation is not enforced, the protective value of encryption is substantially reduced. The template should include specific questions about key storage location, rotation frequency, and access controls on key management systems.
Evaluating Encryption in Shared Responsibility Models
Cloud storage environments operate under a shared responsibility model, where the provider secures the infrastructure and the customer is responsible for data security within that infrastructure. This distinction affects how encryption controls are assessed. The template should document which encryption responsibilities fall to the organization versus the provider and verify that the organization has implemented its required controls rather than assuming the provider has addressed all encryption needs. This is a common point of confusion that assessments need to surface explicitly.
Logging, Monitoring, and Incident Detection
Visibility into cloud storage activity is a prerequisite for detecting unauthorized access, configuration changes, and data exfiltration. NIST SP 800-53 includes the AU control family, which addresses audit logging, log review, and audit record protection. ISO 27001 Annex A.12.4 covers monitoring of system use and log management. A cloud storage risk assessment template should verify that logging is enabled across all storage assets, that logs are retained for the required duration, and that alerts are configured for defined anomalous behaviors.
The assessment should also evaluate whether log data is being reviewed in practice. Many organizations enable logging but do not establish a review process, which means suspicious activity goes undetected until a separate incident surfaces it. The template should include questions about review frequency, responsible parties, and integration with the organization’s broader security monitoring environment.
Vendor and Third-Party Risk Considerations
Cloud storage risk does not exist solely within an organization’s own configurations. Third-party vendors, development partners, and managed service providers often have access to cloud storage environments as part of contractual arrangements. ISO 27001 Annex A.15 addresses supplier relationships directly, requiring organizations to assess and manage the security risks introduced by third parties. NIST SP 800-161 provides supply chain risk management guidance relevant to cloud vendor relationships.
A cloud storage risk assessment template should include a section evaluating third-party access, the contractual security requirements applied to vendors, and whether those requirements are being verified through periodic reviews or audits. This section should also address data processing agreements, particularly where cloud storage holds personal data subject to privacy regulations.
Conclusion
Building a cloud storage risk assessment that aligns with NIST and ISO 27001 is not primarily a technical exercise. It is a documentation and governance exercise that requires organizations to be explicit about what data they hold, how it is protected, who is responsible for it, and how they will know when something goes wrong. The template is the mechanism that makes this explicit. Without it, cloud storage environments are assessed informally and inconsistently, which creates exactly the kind of ambiguity that compliance frameworks are designed to eliminate.
The sections described throughout this article — data classification, access control, encryption, logging, and third-party risk — are not an exhaustive list of everything a cloud storage risk assessment might address. They are the categories that NIST and ISO 27001 identify as foundational, and they represent the minimum that any credible assessment should cover. Organizations that build their templates around these control categories will produce assessments that are both operationally useful and defensible under external review. That combination is what turns a risk assessment from a compliance exercise into a practical tool for managing cloud storage environments with consistency and confidence.


In the realm of industrial safety and regulatory adherence, compliance plates play a crucial role. Compliance Plates Australia offers comprehensive engineering solutions designed to ensure that machinery, equipment, and installations across Australia meet stringent regulatory requirements. These innovative solutions are tailored to both standard and custom compliance plate needs, providing organisations with reliable and durable identification systems.
Understanding Compliance Plates
Compliance plates are essential markers affixed to equipment and installations, conveying critical information such as manufacturing details, safety data, load ratings, and certification status. These plates facilitate compliance with Australian safety standards and assist in maintenance, servicing, and inspections.
The Importance of Compliance Plates in Australian Industry
Industries ranging from construction, mining, manufacturing, to infrastructure depend heavily on compliance plates. They verify that the equipment meets legal safety standards and provide traceability for quality control. Failure to comply can result in significant legal penalties and operational risks, making the role of compliant and clear signage indispensable.
Innovations in Design and Materials
Compliance Plates Australia utilises cutting-edge materials that enhance durability and resistance to harsh environmental conditions. Their plates are manufactured from aluminium, stainless steel, and specialised plastics, each selected according to the specific application requirements. This innovation ensures longevity and readability, even in extreme weather or corrosive environments.
Advanced printing technologies such as laser etching and UV printing are employed to produce permanent, high-resolution inscriptions. These methods prevent fading, scratching, or peeling, thereby guaranteeing the compliance plates remain legible throughout their lifespan.
Custom Engineering Solutions for Diverse Applications
Standard compliance plates often require adaptation to suit unique industrial equipment or machinery. Compliance Plates Australia excel in delivering custom engineering solutions. Their expert team collaborates with clients to develop bespoke plates that conform to exact specifications, including size, shape, content, and attachment methods.
This bespoke approach ensures that every compliance plate not only meets legislative requirements but integrates seamlessly with the equipment’s design and operational environment.
Integration of Compliance Plates into Asset Management
Beyond identification, compliance plates can be incorporated into broader asset management systems. By combining physical plates with digital documentation, organisations gain enhanced control over equipment maintenance and lifecycle tracking. Compliance Plates Australia supports clients in implementing these systems, improving compliance verification and operational efficiency.
Ensuring Regulatory Compliance in Australia
The Australian regulatory landscape mandates strict adherence to safety standards, which vary across states and industry sectors. Compliance Plates Australia stays abreast of these constantly evolving regulations. Their engineering solutions ensure that all compliance plates are manufactured and installed in accordance with the latest legislative frameworks, thus protecting businesses from non-compliance risks.
Consultation and Technical Support
Providing engineering solutions transcends mere production; it includes expert consultation and ongoing technical support. The team at Compliance Plates Australia offers clients valuable guidance on plate selection, placement, and maintenance, ensuring maximum effectiveness and compliance.
Applications Across Industries
Compliance Plates Australia’s solutions cater to a broad spectrum of industries. In construction, they develop durable plates that withstand physical impacts and weather extremes. The mining sector benefits from plates resistant to chemical exposure and abrasion. In manufacturing, they supply precision-engraved markers for machinery safety and performance specifications.
Each industry’s needs are carefully studied to deliver plates that are fit for purpose, ensuring safety and regulatory conformance across all operational environments.
Technological Advances Supporting Compliance
In recent years, technological advances have enhanced the functionality of compliance plates. Features such as QR codes and RFID tags are being integrated to allow real-time data access and tracking. Compliance Plates Australia is at the forefront of these innovations, offering options that enable businesses to harness digital solutions for enhanced operational control.
Environmental Considerations
Environmental sustainability is a significant consideration in modern engineering. Compliance Plates Australia employs eco-friendly materials and processes wherever feasible. The longevity of the plates themselves contributes to reduced waste and resource consumption, aligning with broader corporate social responsibility objectives.
Ordering and Delivery Process
The company’s streamlined ordering process ensures efficient turnaround times. Clients can provide specifications through an easy-to-use interface, and the expert team manages design, production, and delivery. This systematic approach reduces downtime, optimising operational continuity for businesses.
Training and Education Services
Understanding the importance of compliance plate usage, Compliance Plates Australia also offers training services. These sessions educate staff on the correct installation, inspection, and maintenance of plates, further reinforcing workplace safety and adherence to regulatory standards.
Global Standards and Local Expertise
While compliance plates must meet Australian standards, many organisations operate internationally. Compliance Plates Australia’s engineering solutions consider global best practices, enabling clients to maintain comprehensive compliance across border operations without compromising local requirements.
Future Trends in Compliance Plates
Looking forward, innovation in smart technologies and materials will continue to shape the compliance plate landscape. Customisable digital solutions and increased integration with asset management systems represent key trends. Compliance Plates Australia is committed to pioneering these developments, providing clients with future-ready engineering solutions.
Conclusion
Compliance Plates Australia exemplifies industry leadership in the provision of engineering solutions for compliance plates. Their innovative designs, materials expertise, and customised services ensure that Australian businesses can meet and exceed safety and regulatory standards. By choosing Compliance Plates Australia, organisations invest in reliability, compliance, and operational excellence.

Starting a career in customer service or a call center can be a practical choice for people who enjoy communicating with others, solving problems, and working in a fast moving environment. These jobs are available in many industries, from retail and banking to travel, technology, healthcare, and online businesses.
If you’re thinking about this career path, you might be wondering where to start, what skills employers want, and how to find the right position. The good news is that you don’t always need years of experience to get started. With the right approach, you can find an entry level role and build useful skills along the way.
Understanding Customer Service and Call Center Careers
Customer service jobs are mainly about helping customers. That might mean answering questions, handling complaints, explaining products, checking orders, or helping someone solve a technical issue.
Call center positions often involve speaking with customers over the phone, although many modern companies also use email, live chat, and social media support. Some roles are focused on incoming calls, while others involve contacting customers about products, services, surveys, or appointments.
The work can be different from one company to another. A customer service representative at an online store may spend most of the day helping with orders and returns. Someone working for a telecommunications company could be dealing with billing questions or technical problems.
Before you begin your search, think about what type of work sounds comfortable for you. Do you prefer helping people with problems? Are you comfortable talking on the phone? Would you rather communicate through chat or email? These simple questions can help narrow down your options.
Skills Employers Usually Look For
You don’t necessarily need a university degree for many customer service or call center positions. Employers often pay close attention to communication skills, patience, reliability, and your ability to stay calm when dealing with difficult situations.
Clear communication is especially important. Customers want simple answers, not complicated explanations. You should be able to listen carefully and explain information in a way that’s easy to understand.
Basic computer skills can also make a big difference. Many representatives use customer relationship management systems, ticketing platforms, spreadsheets, email software, and internal databases throughout the day.
Another useful skill is problem solving. Customers may not always explain an issue clearly, so you’ll need to ask the right questions and figure out what they actually need.
Language skills can also open additional opportunities. Companies that serve international customers may look for people who can communicate confidently in more than one language.
How to Start Your Job Search
Once you’ve decided what kind of position you want, it’s time to start searching. Online job platforms can be a useful place to find customer service and call center openings. You can search using terms such as customer service representative, call center agent, customer support specialist, technical support representative, or help desk associate.
When you’re ready to หางาน, don’t simply apply to every position you see. Read the job description carefully. Check the required skills, working hours, location, salary information, and experience requirements.
If a position looks suitable, prepare your application before you สมัครงาน. Your resume should clearly show your communication skills, previous work experience, computer knowledge, and any experience involving customers.
Even if you’ve never worked in a call center before, you may have transferable experience. Retail work, hospitality, sales, reception, administration, and even volunteer activities can demonstrate useful communication and problem solving abilities.
Preparing for a Customer Service Interview
Getting an interview is only the first step. Preparation can make you feel much more confident.
Customer service interviews often include questions about how you would handle difficult customers or stressful situations. For example, an interviewer might ask what you’d do if a customer became angry about a delayed order.
A good answer should show patience and professionalism. Explain that you’d listen carefully, understand the customer’s concern, check the available information, and offer an appropriate solution based on company policy.
You may also be asked about teamwork, handling multiple tasks, or meeting performance targets. Think about real situations from your previous experience that demonstrate these abilities.
For some call center jobs, employers may also test your speaking skills, typing speed, computer knowledge, or language ability.
Building a Long Term Career
A customer support activity does not necessarily be the final vacation spot of your career. It can be a starting point.
After gaining revel in, you might circulate into senior customer support, fine assurance, schooling, team management, income, account control, or operations. Some people sooner or later pass into management positions after developing robust expertise of the commercial enterprise.
The key’s to maintain getting to know. Pay attention to customer comments, improve your communique, study the company’s systems, and grow to be cushty coping with one-of-a-kind forms of situations.
Customer carriers can educate you about abilities which can be useful almost everywhere. You discover ways to talk, manage stress, clear up issues, paintings with a team, and apprehend what customers genuinely need.
Finding the Right Opportunity
Not every name center or customer service role will be the same, so take it slow when evaluating possibilities. Look past the activity title and keep in mind the organization’s painting environment, time table, training, blessings, growth opportunities, and obligations.
If you are simply starting, an access degree function can come up with valuable revel in and help you find out what sort of career fits you.
The vital aspect is to hold your search centered and practical. Update your resume, enhance your communication talents, prepare for interviews, and preserve applying to roles that fit your skills. With consistency and a willingness to examine, customer service and call center work can come to be the beginning of a far larger career.

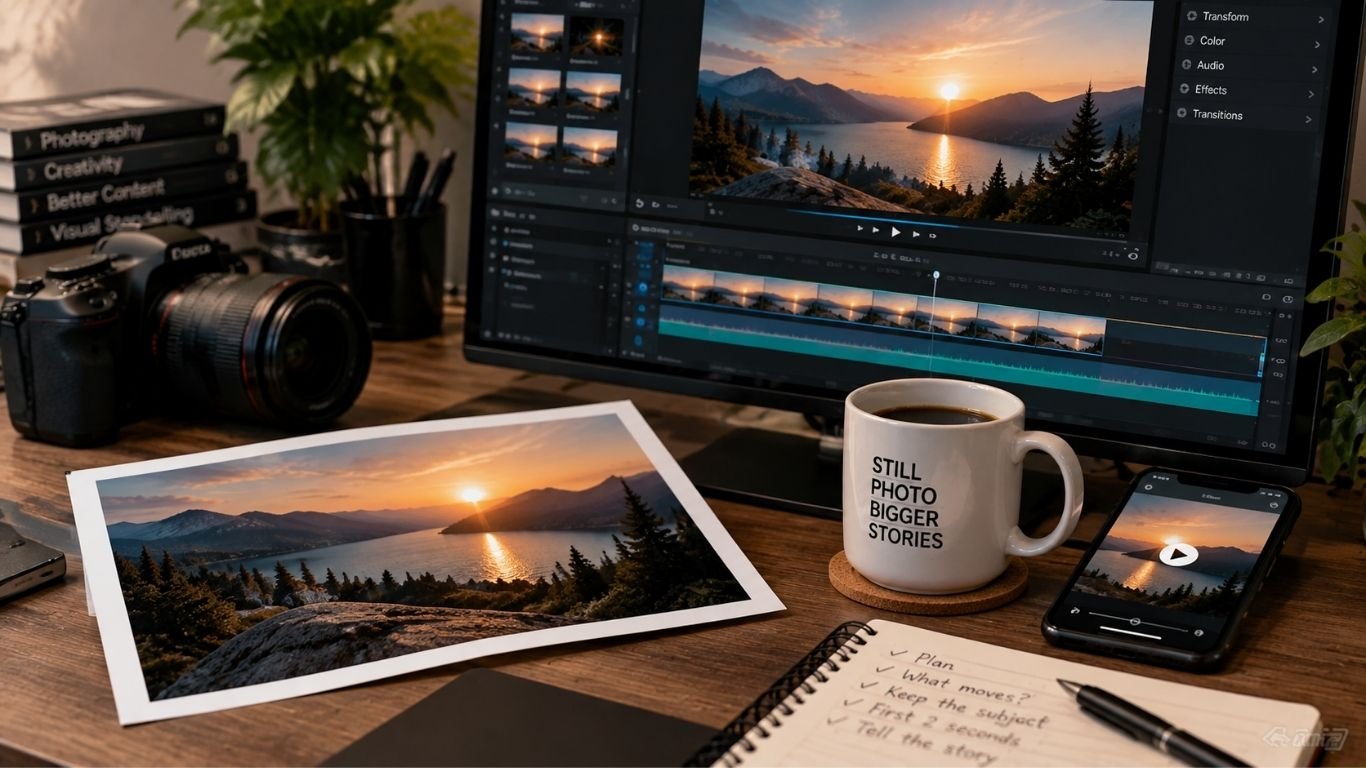
Listicles about “AI video from image” sell a miracle: drop a JPEG, collect a hit. The honest version is duller and more useful. A still is raw material. Motion is a decision about what is allowed to move. The platforms reward a change in the first two seconds. They do not reward a bottle that grows a second label.
If everything in the frame is swimming, nothing is the product. That is why a lot of “viral” generates die in the camera roll. Not because the model is weak. Because nobody named the subject before the pixels started sliding.
The still is already the edit
Most folders are not empty. They are full of packshots, a holiday that never became a Reel, a screenshot of an app that marketing liked in March. Repurposing that pile is the real job. Making a brand-new cinematic universe is the hobby.
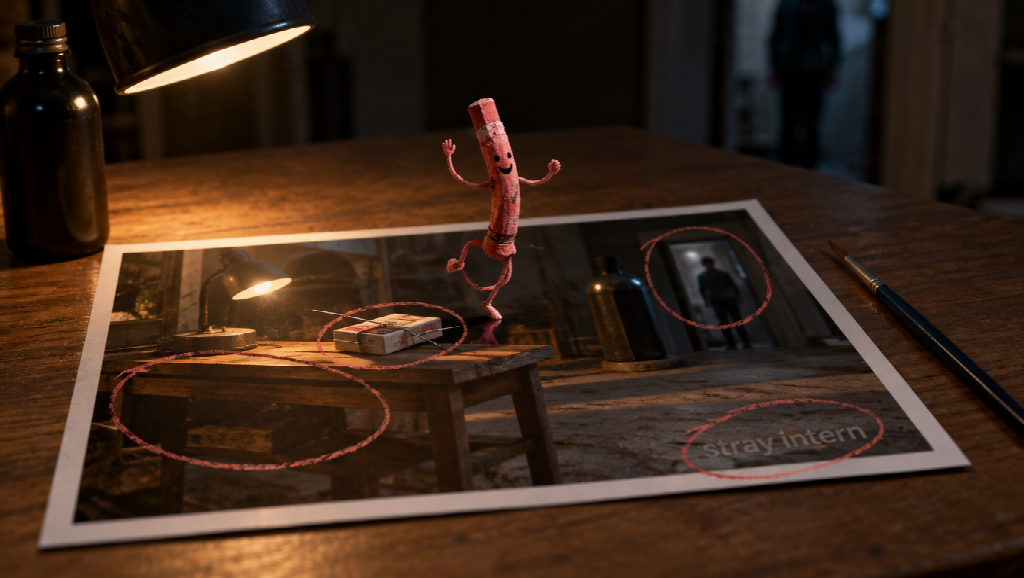
Before anything animates, look at the file the way a merchandiser would. A wire across the pack. Last intern’s watermark. A stranger in a doorway. Animate any of that and you have animated the mistake. AI inpaint is the unglamorous pass: brush only the lie, leave the rest as shot. JPG, PNG, or WEBP. A tight mask. Two references if you are swapping a sign and you actually have the replacement. Free exports may watermark; paid ones can come clean. You still need rights to the original.
Do this first. Motion will not hide a logo you meant to delete. It will make it dance.
Timing is the trick. Identity is the test.
Short feeds punish a slow hello. A push-in, a hold, a light that finds the label — that is often enough. Complexity is how you lose the object. One focal point. Motion that serves it. If the background is more interesting than the SKU, you have made a travel film by accident.
People who live on Reels already know the first beat is a crop, not a plot. The mistake is asking the generator to invent a second room so the clip “feels bigger.” Bigger is how the colour of the cap changes. Keep the room you photographed. Spend the seconds on the thing you sell.
Seedance 2.5 is the model lane for a kit-locked beat: text plus pictures, sometimes a scrap of video or audio, about four to thirty seconds, typically 1080p on a hosted generator — not a 4K poster. You write seconds, not vibes. “0–5s the same still; 5–14s a slow push on the same cap; 14–22s hold for a caption I will type — no extra hands, no second bottle.” If second eighteen grows a necklace, the folder is wrong. Fix the kit. Do not prompt “more viral.”
Iteration still wins over one precious render. Change one variable: crop, duration, or the negative (“no extra table”). Post the take you watched. Count what happened. Do not publish a virality forecast you did not measure.
A marketer’s version of the same test is uglier and better. Take last season’s approved packshot, not a prettier table the model invented. Run two lengths. Watch them next to the product page. If they disagree, the page wins. That is repurposing. “Make it scroll-stopping” is how the shade name drifts.
What this is not
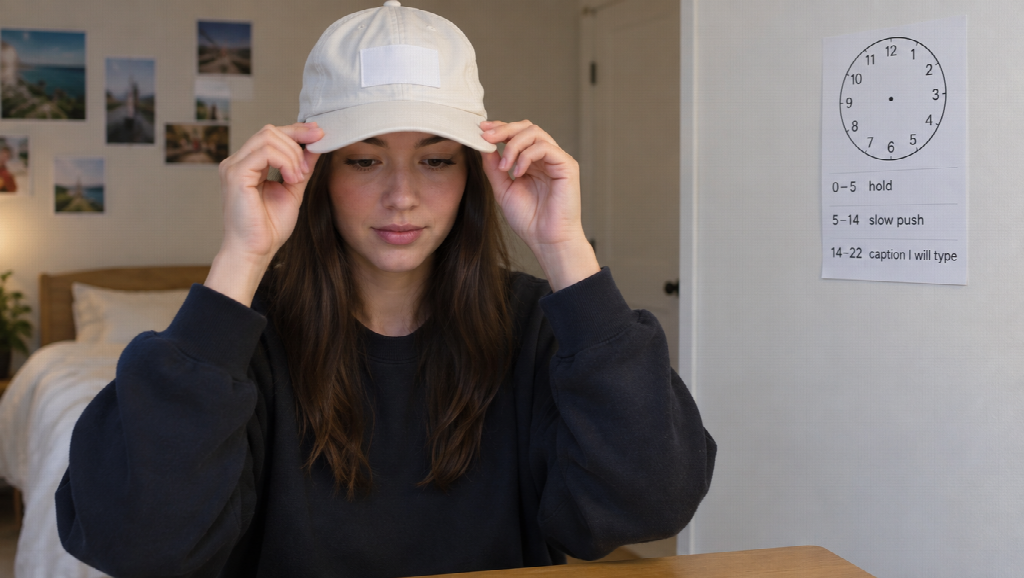
It is not a face-swap toy and not a promise that the algorithm owes you a spike. It is not a substitute for the photograph you do not own. Credits are studio time you did not book.
The useful shift is the one the listicles bury under “top tools.” Images stopped being endpoints. They became assets you can spend twice — if the subject survives the spend. Clean the frame. Time the motion. Keep the object. The feed can decide the rest.

Why Your Headphones Pick Up the Whole Office on Calls

Transform Your Skin with RF Microneedling: Discover the Benefits at Elite Body Contouring

Revolutionizing Precision: The Advantages of Fiber Optic Laser Cutting with Macro Weld

Stunning Spring Carnival Dresses to Elevate Your Style This Season

Top Cricket Equipment Essentials Every School Should Have

Innovative Architects in Sydney: Designing Your Dream Space with Shore Architects

How to Ensure Your Home is Valued Correctly for a Quick Sale
Christopher Dare: The Untold Story of Engineer and Former Husband of Angela Rippon

The 15 Highest-Paid Rugby Players in the World

What Is Fanquer? The Digital Creator Platform Transforming Direct-to-Fan Engagement

Dr Jared Ross: Missouri Appeals Court Upholds Protection Order Over Graphic Torture and Murder Threats
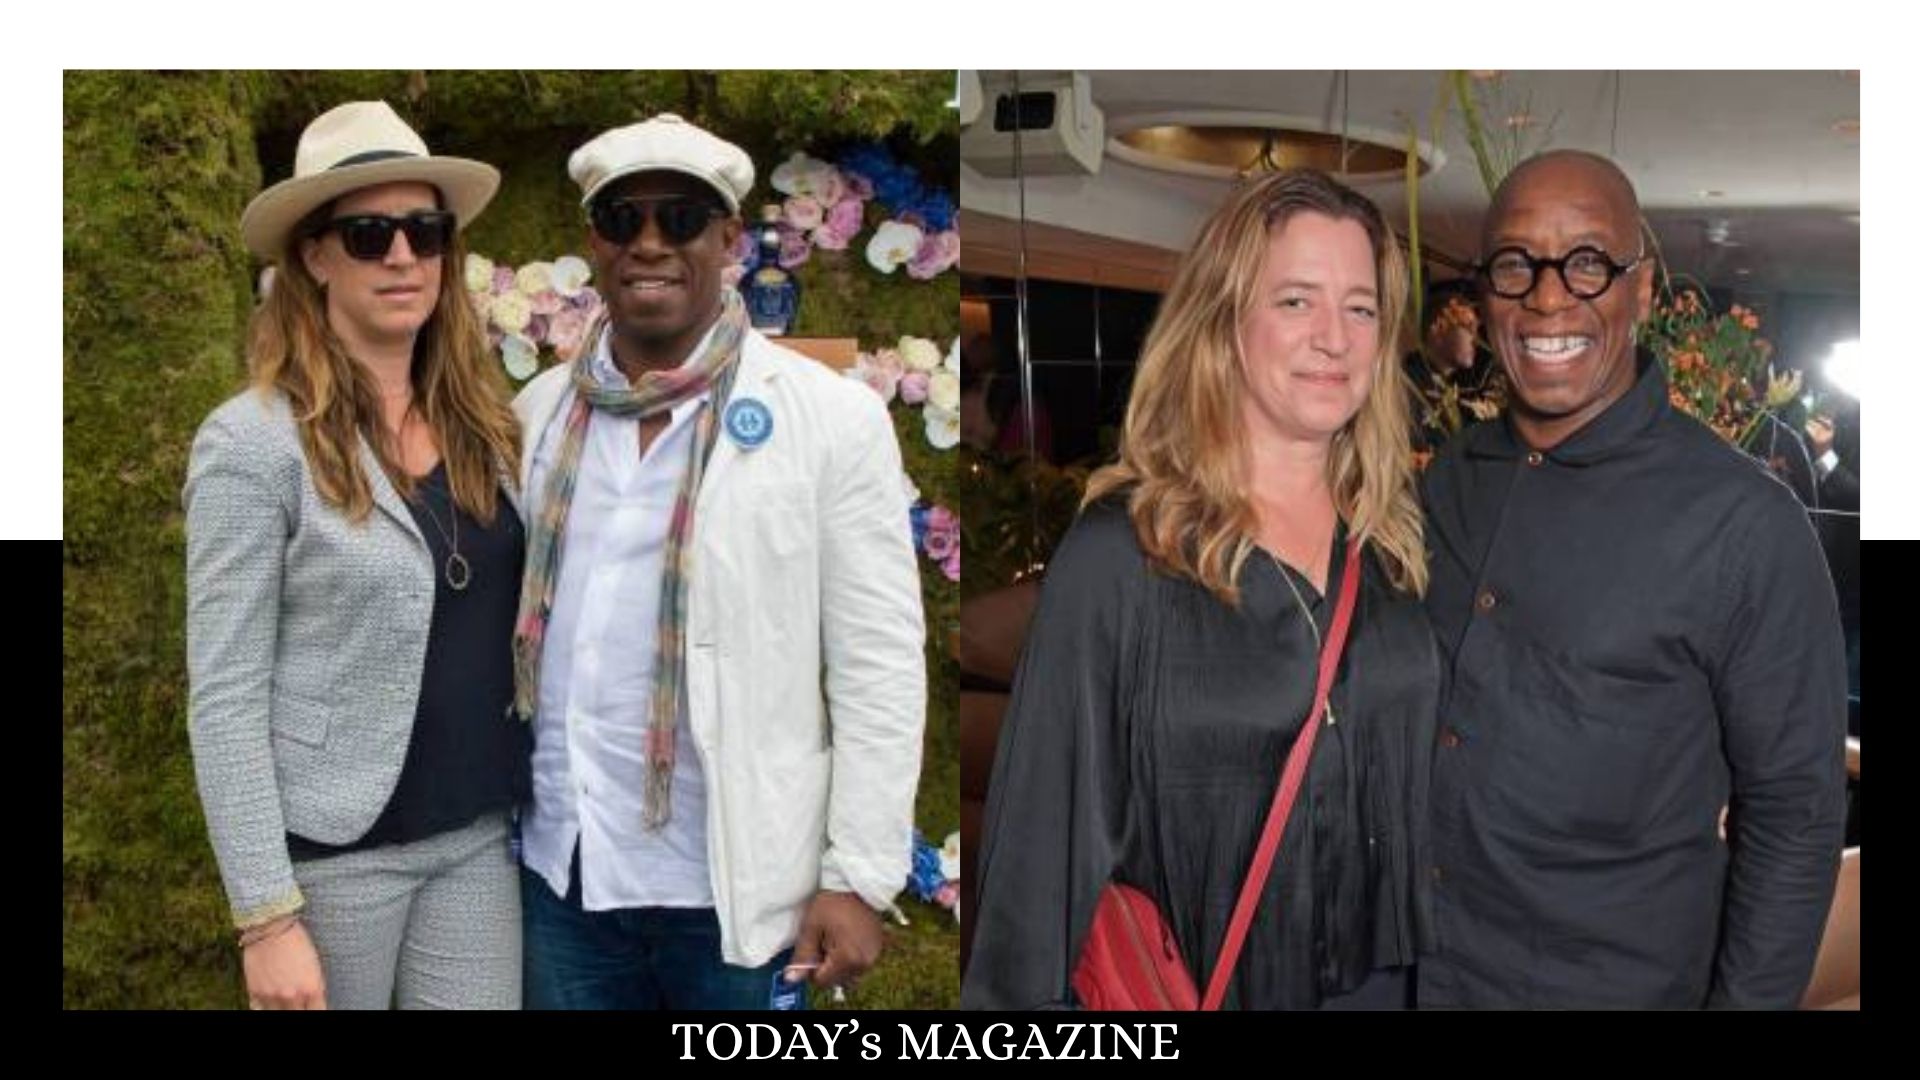
Nancy Hallam: The Inspiring Life, Career, and Success Story Behind Ian Wright’s Wife
How to Ensure Your Home is Valued Correctly for a Quick Sale
Christopher Dare: The Untold Story of Engineer and Former Husband of Angela Rippon
The 15 Highest-Paid Rugby Players in the World
What Is Fanquer? The Digital Creator Platform Transforming Direct-to-Fan Engagement
Dr Jared Ross: Missouri Appeals Court Upholds Protection Order Over Graphic Torture and Murder Threats
Nancy Hallam: The Inspiring Life, Career, and Success Story Behind Ian Wright’s Wife
-
 Real Estate9 months ago
How to Ensure Your Home is Valued Correctly for a Quick Sale
-
Celebrity11 months ago
Christopher Dare: The Untold Story of Engineer and Former Husband of Angela Rippon
-
 Sports5 months ago
The 15 Highest-Paid Rugby Players in the World
-
 Technology5 months ago
What Is Fanquer? The Digital Creator Platform Transforming Direct-to-Fan Engagement
-
 Celebrity5 months ago
Dr Jared Ross: Missouri Appeals Court Upholds Protection Order Over Graphic Torture and Murder Threats
-
Celebrity12 months ago
Nancy Hallam: The Inspiring Life, Career, and Success Story Behind Ian Wright’s Wife
-
 Celebrity8 months ago
Who Is Azriel Crews? Inside the Life and Career of Terry Crews’ Daughter
-
 Celebrity11 months ago
Who Is Maisie Mae Roffey? The Private Life, Family Story, and Quiet Success of Julie Walters’ Daughter